


- #githubactions
- #security
- #cicd
One Stolen Token Should Not Ship Your App
One stolen admin token reached every repo. So I built a release that needs two people, and found four bugs only by running it.

The UI gets the applause. The backend gets the blame when something breaks. The obsession here? Making sure it doesn't — secure auth, clean migrations, event-driven systems, and infrastructure that scales without waking anyone up at 3AM. Backend by choice. DevOps by design.

Backend | DevOps · Open Source ↗
Life would be easier if I had the source code.
Some shipped. Some still cooking.
Real-time parcel logistics engine: state-machine routing, rider dispatch, and signature-verified webhook notifications.


Offline-first field operations platform: GPS-stamped photo capture, fraud detection heuristics, and tamper-evident audit logs for remote teams.
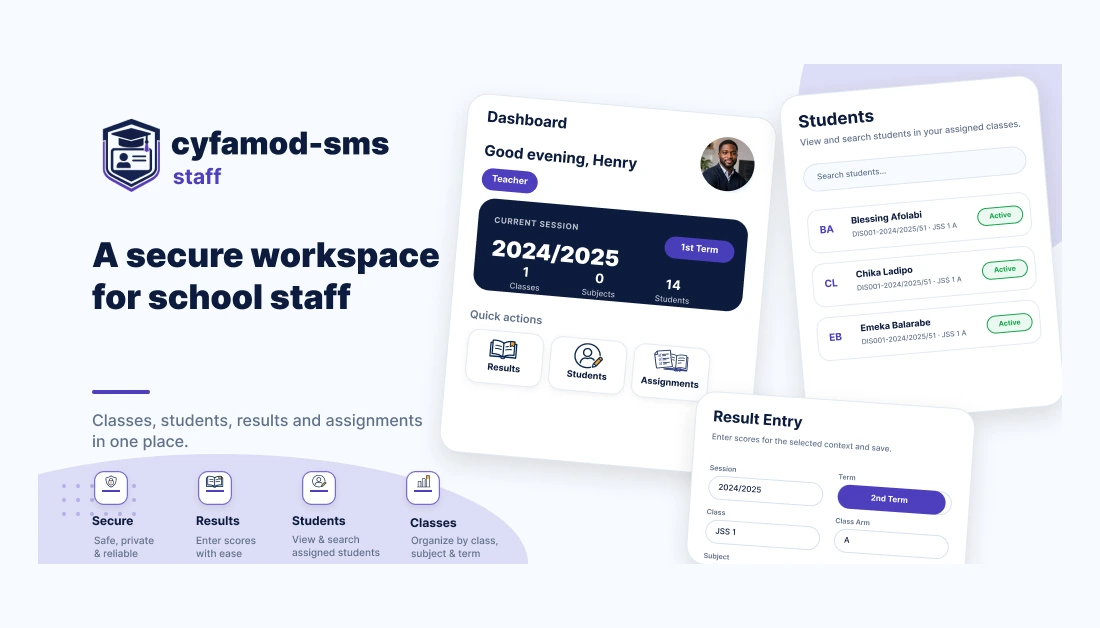
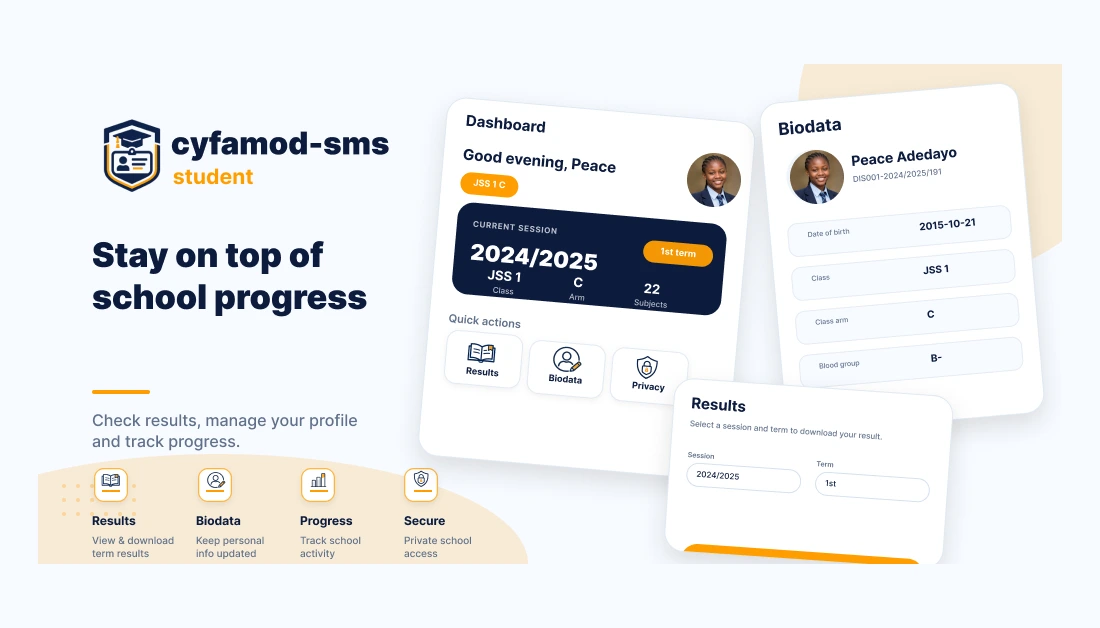


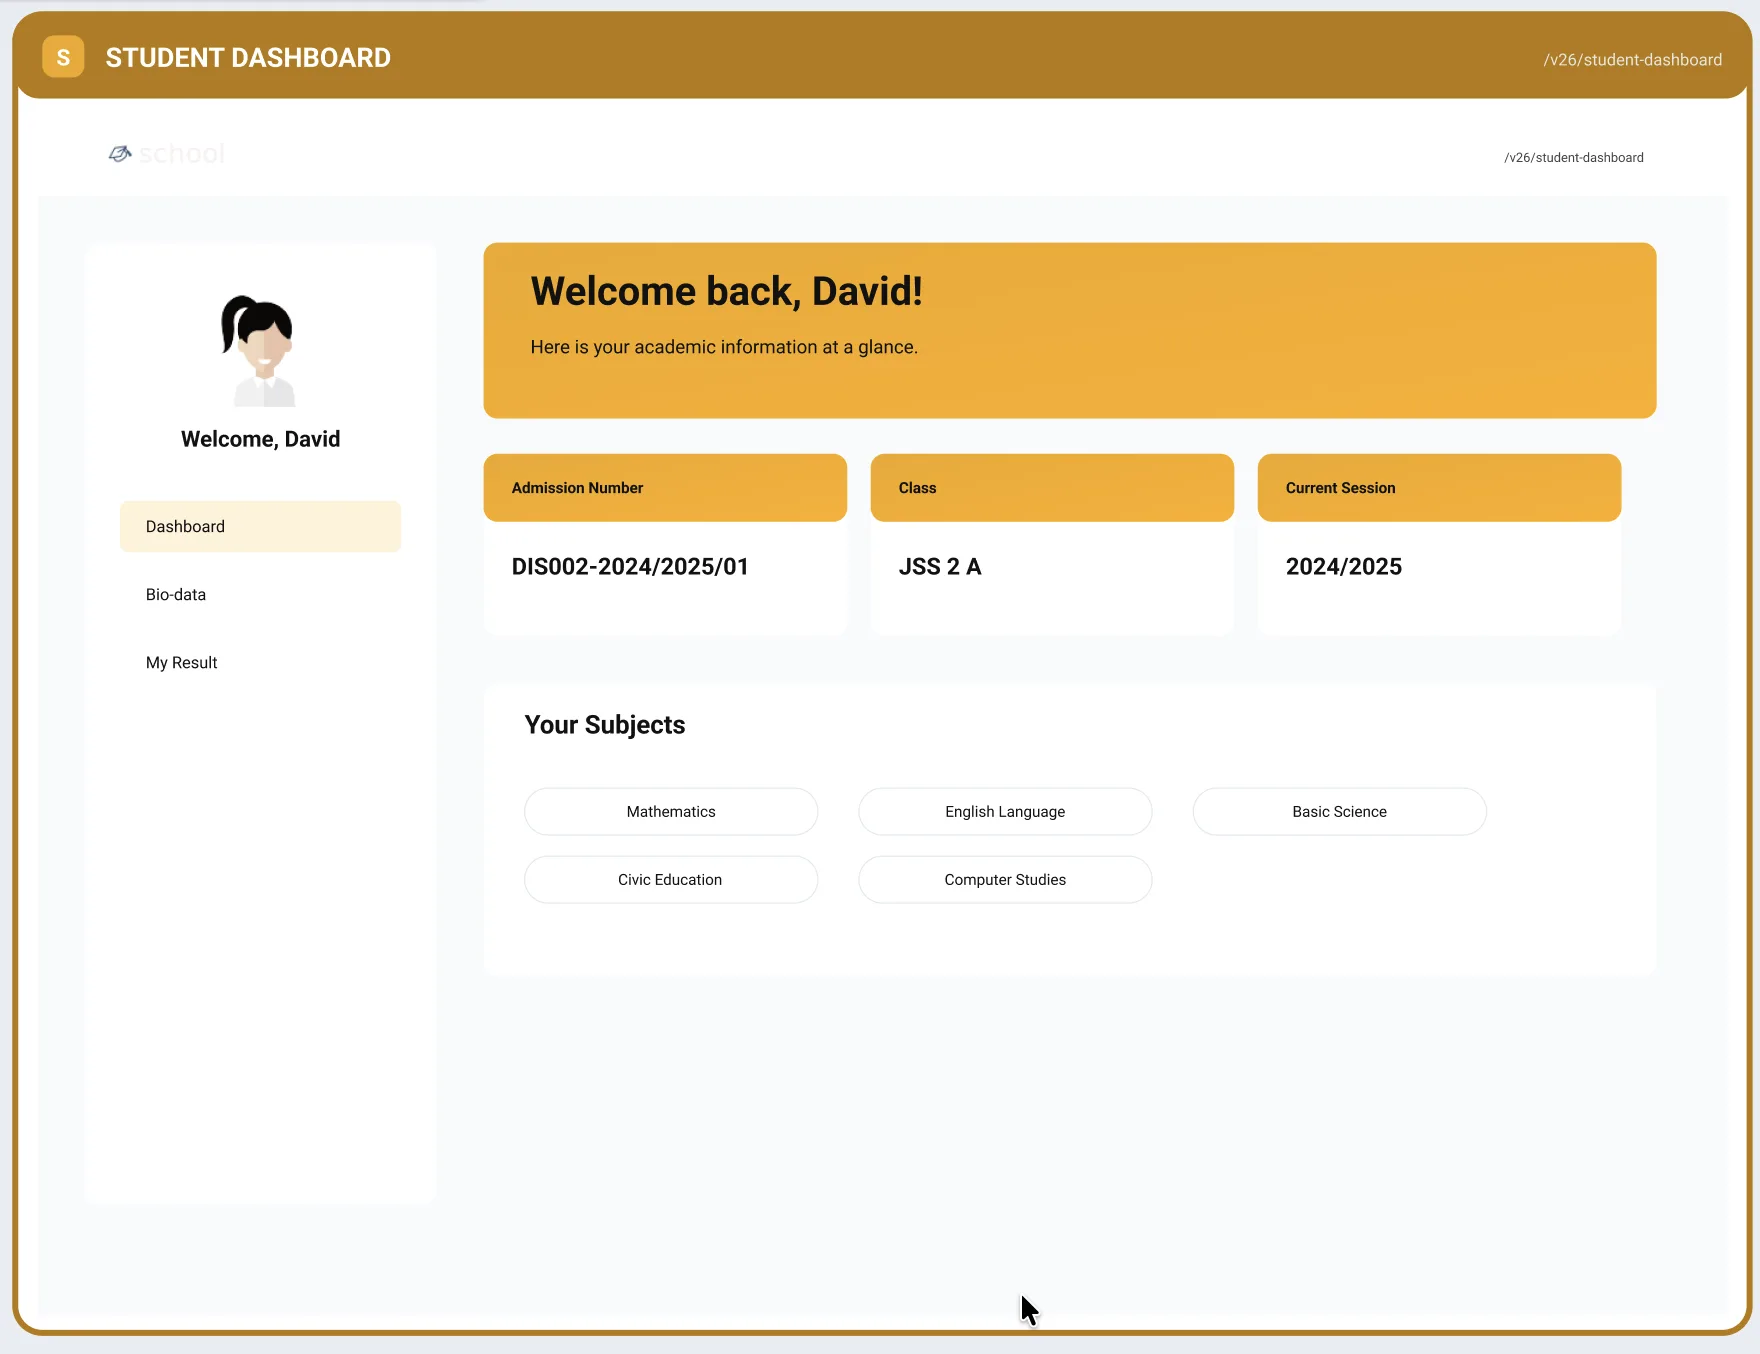
Multi-tenant school ERP: web admin portals plus live Google Play apps for teacher grading, student report cards, and parent fee tracking.
⚡ Moving 200+ users between channels manually took 2+ hours
→ Bulk-migrates with exclusion lists & emoji announcements in 30 seconds
⚡ Critical Slack messages silently deleted during rollover windows
→ Monitors deletions, posts visible alerts naming the culprit
⚡ Manual management of exclusive community reward codes
→ Generates unique codes via Telegram, verifies membership
⚡ Missing high-value tweet reply windows without burning API quota
→ Monitors 50+ accounts via RSS, fires Telegram alerts
⚡ Chaotic group chats with no structured Q&A data for analysis
→ Scrapes multiple groups, exports to Google Sheets
⚡ Cross-language service communication with proper fault tolerance
→ FastAPI/Flask + Express with service discovery
⚡ Promotional emails burying important messages in Gmail
→ Detects promos via patterns, bulk deletes with dry-run mode
⚡ Tedious manual checkout flows on e-commerce platforms
→ Stealth browser product selection and automated billing
⚡ Commits pushed after a PR merged never made it to dev — silently
→ Audits any repo list, flags orphaned commits before they're lost
⚡ GlassWorm supply-chain attack hiding invisible Unicode payloads in VS Code extensions
→ Scans macOS, Linux & Windows for C2 patterns and credential-theft indicators
⚡ Stale node_modules, old venvs, and AI logs quietly eating disk space
→ Automated cleanup, plus a "Vampire Audit" for high-CPU processes
⚡ Setting branch protection manually, repo by repo, across an org
→ Applies branch protection rules org-wide in one run
⚡ Paid transcription APIs for audio that could stay fully local
→ Offline macOS transcription, no API key needed
⚡ Uploading or purging hundreds of workspace emoji one by one
→ Bulk-uploads and mass-deletes emoji via the Slack Admin API
Real-time parcel logistics engine: state-machine routing, rider dispatch, and signature-verified webhook notifications.
Offline-first field operations platform: GPS-stamped photo capture, fraud detection heuristics, and tamper-evident audit logs for remote teams.
Multi-tenant school ERP: web admin portals plus live Google Play apps for teacher grading, student report cards, and parent fee tracking.
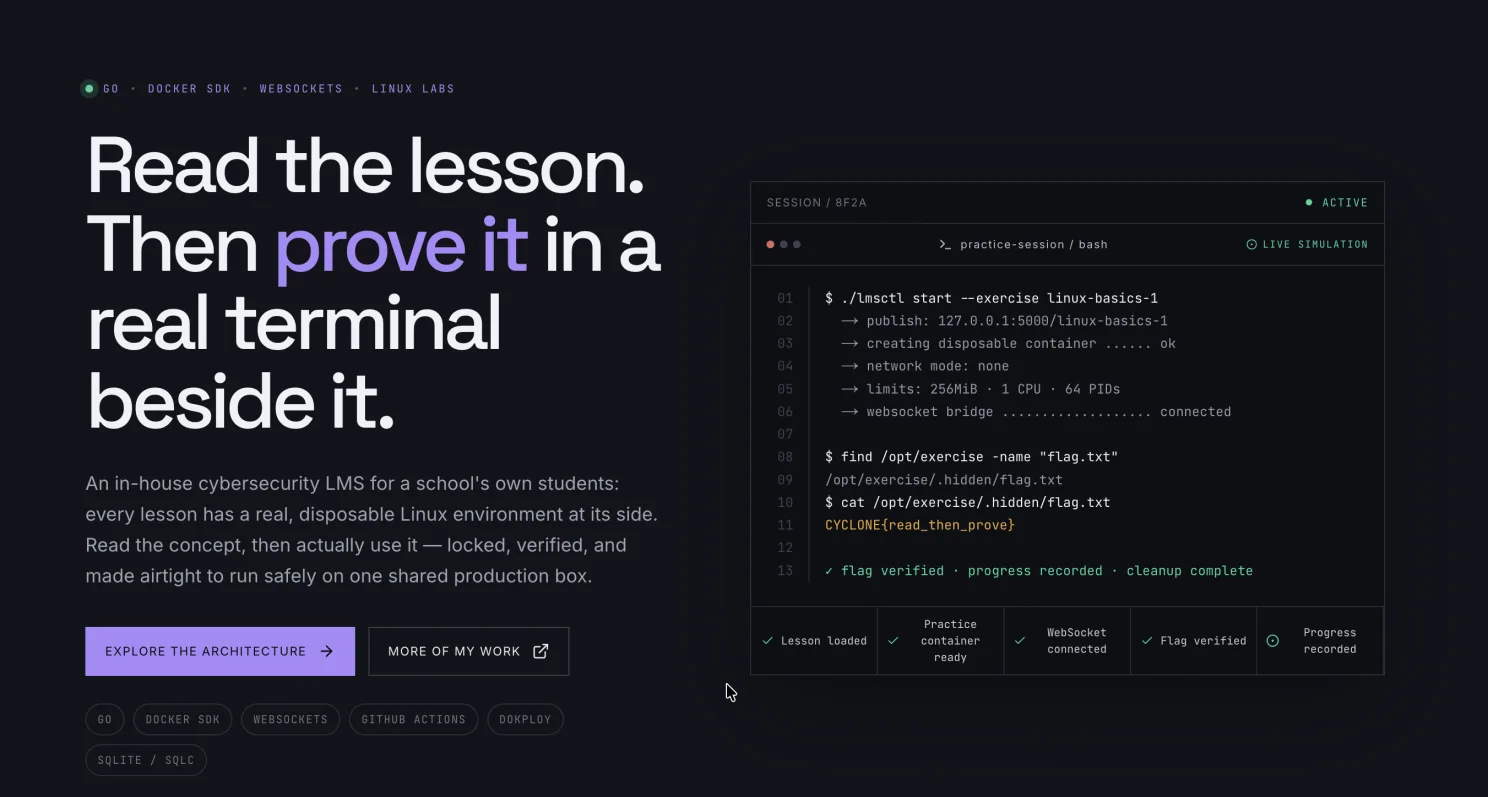
Disposable browser-based Linux labs — a Go + Docker SDK engine that spawns isolated practice containers, streams shells over WebSockets, and self-healed when production cleanup pruned its image cache.
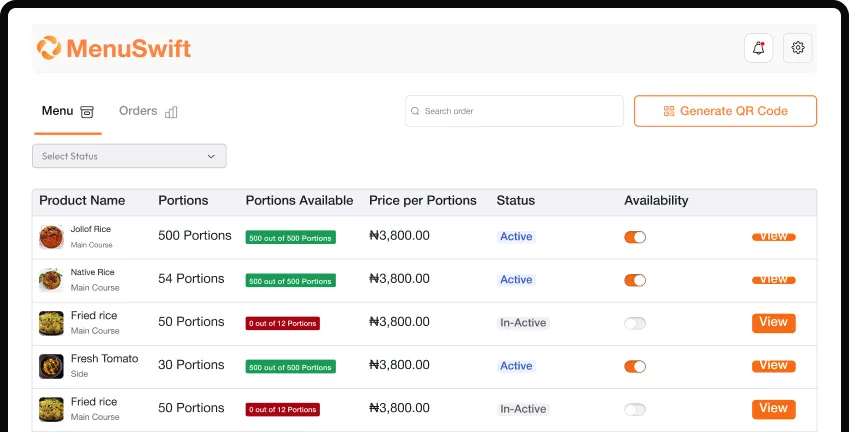
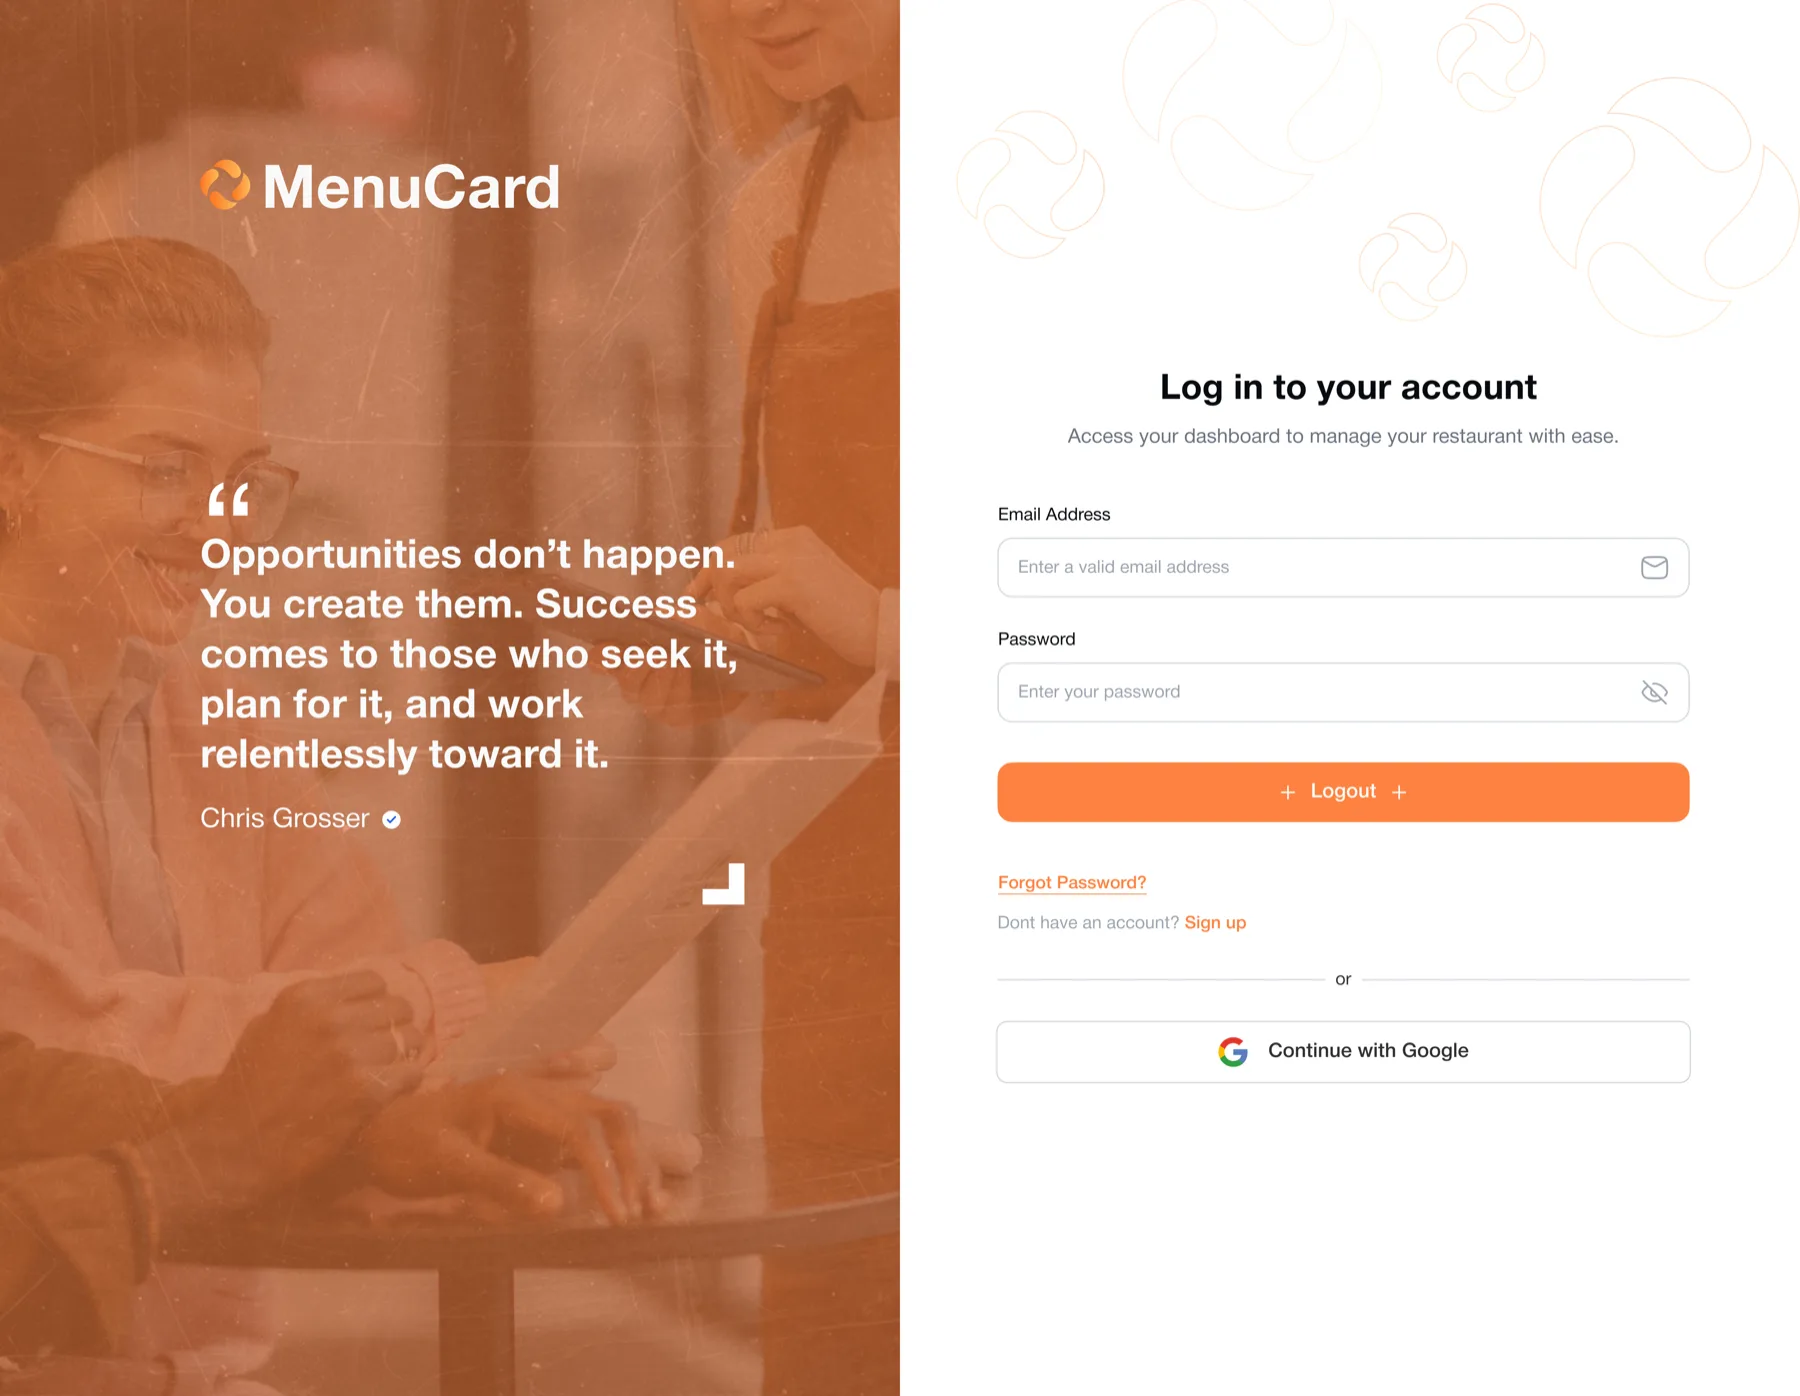
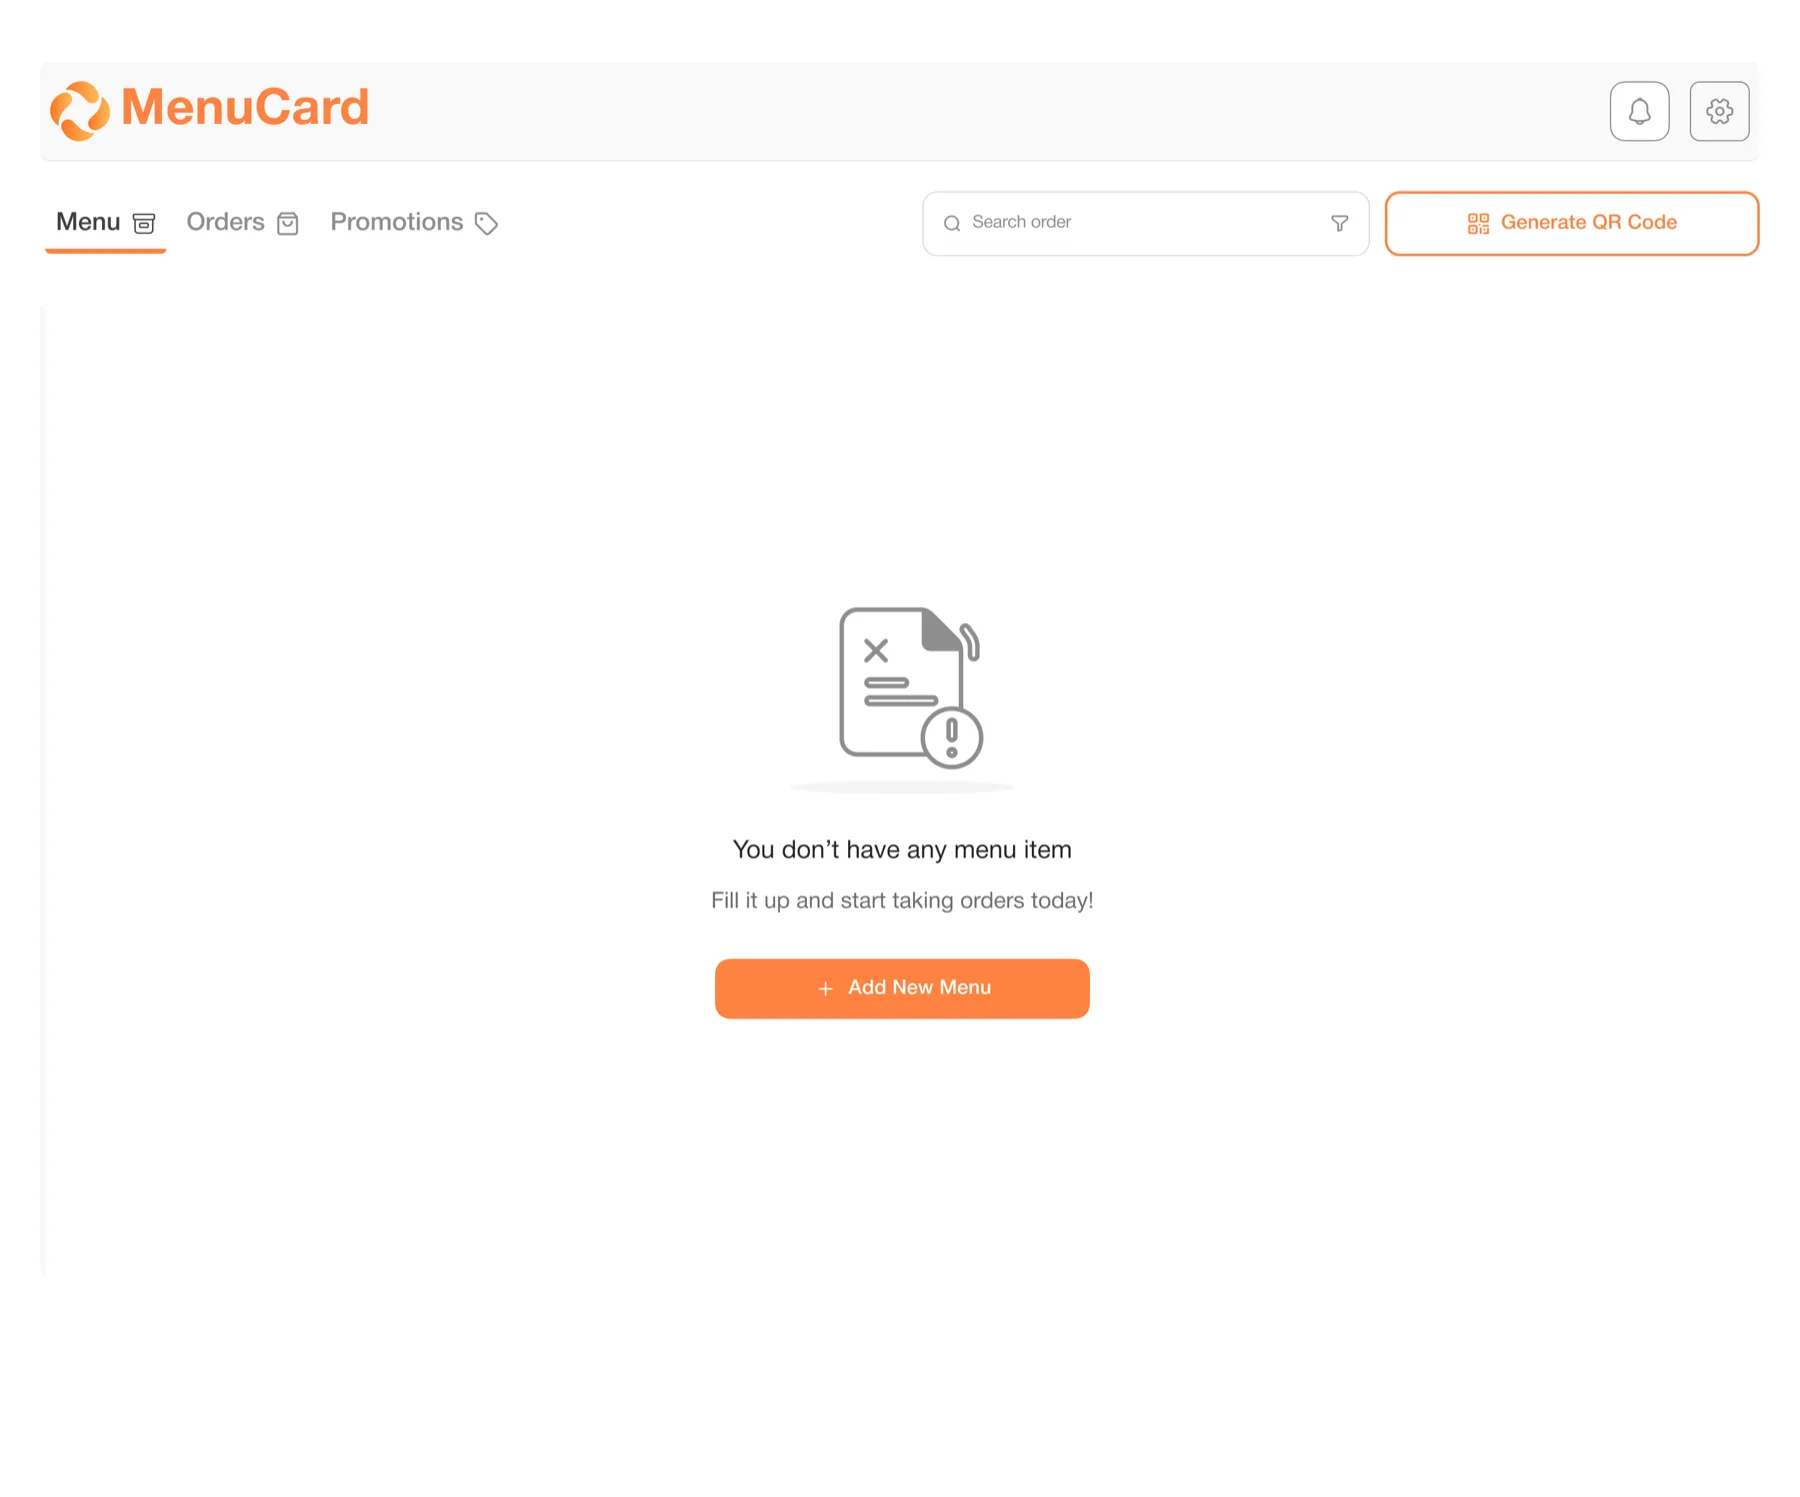
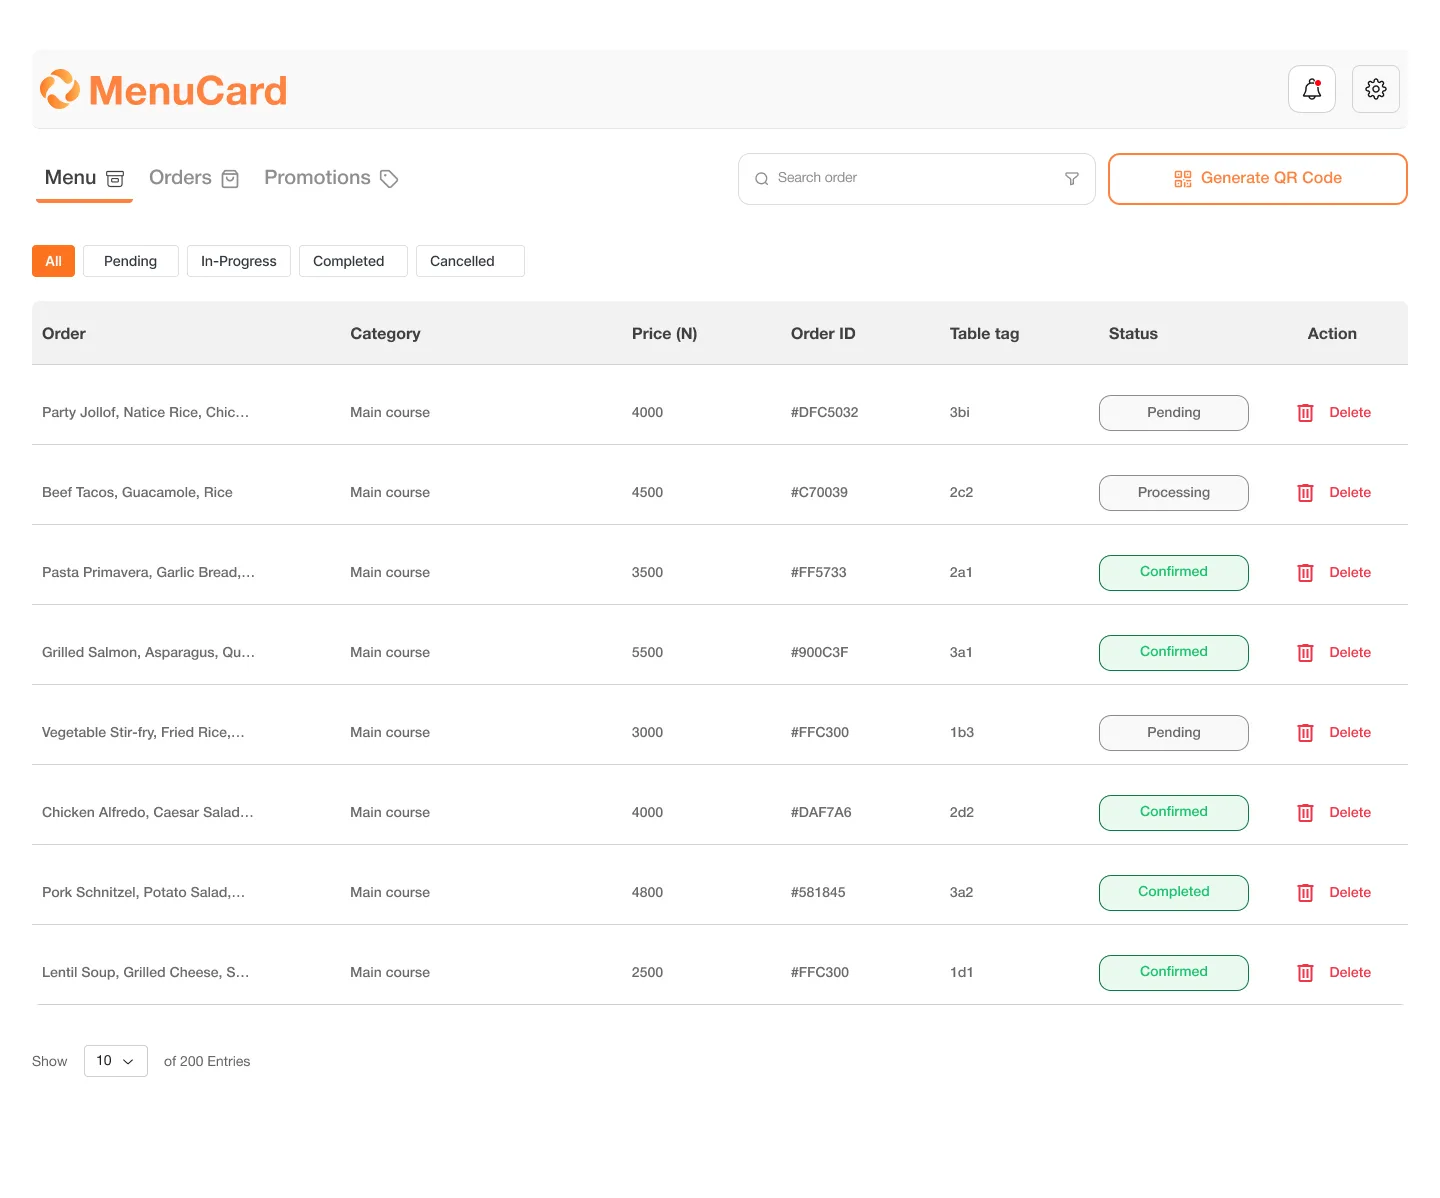
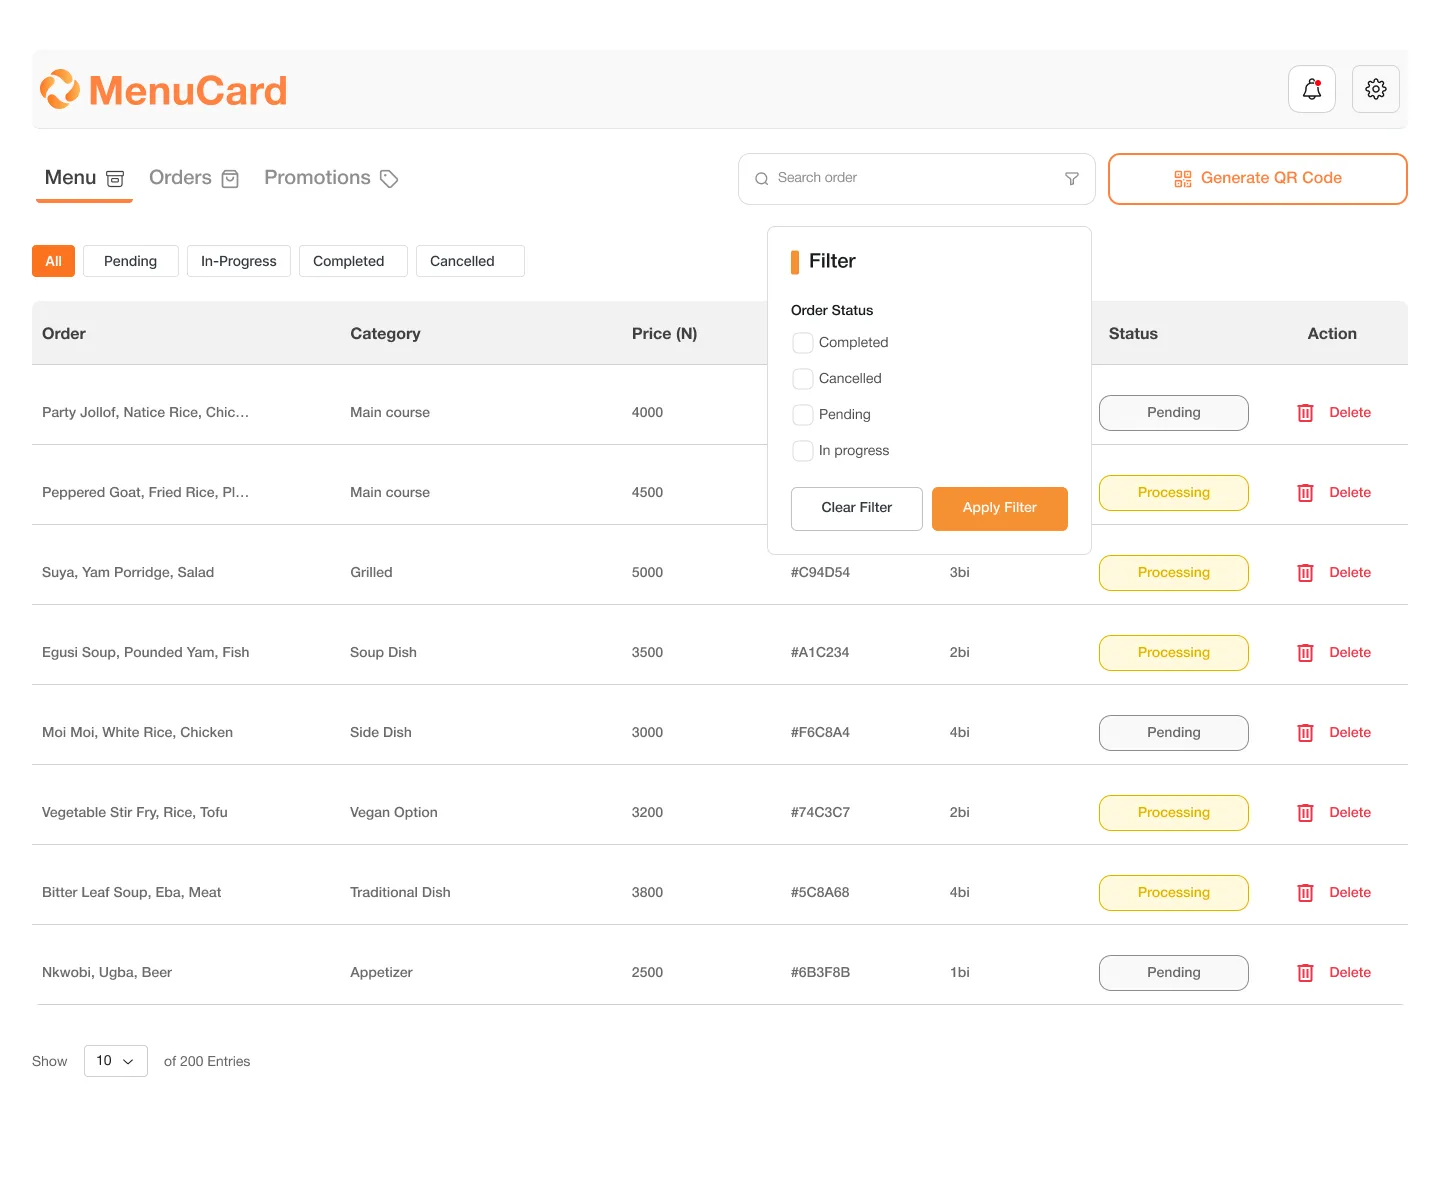


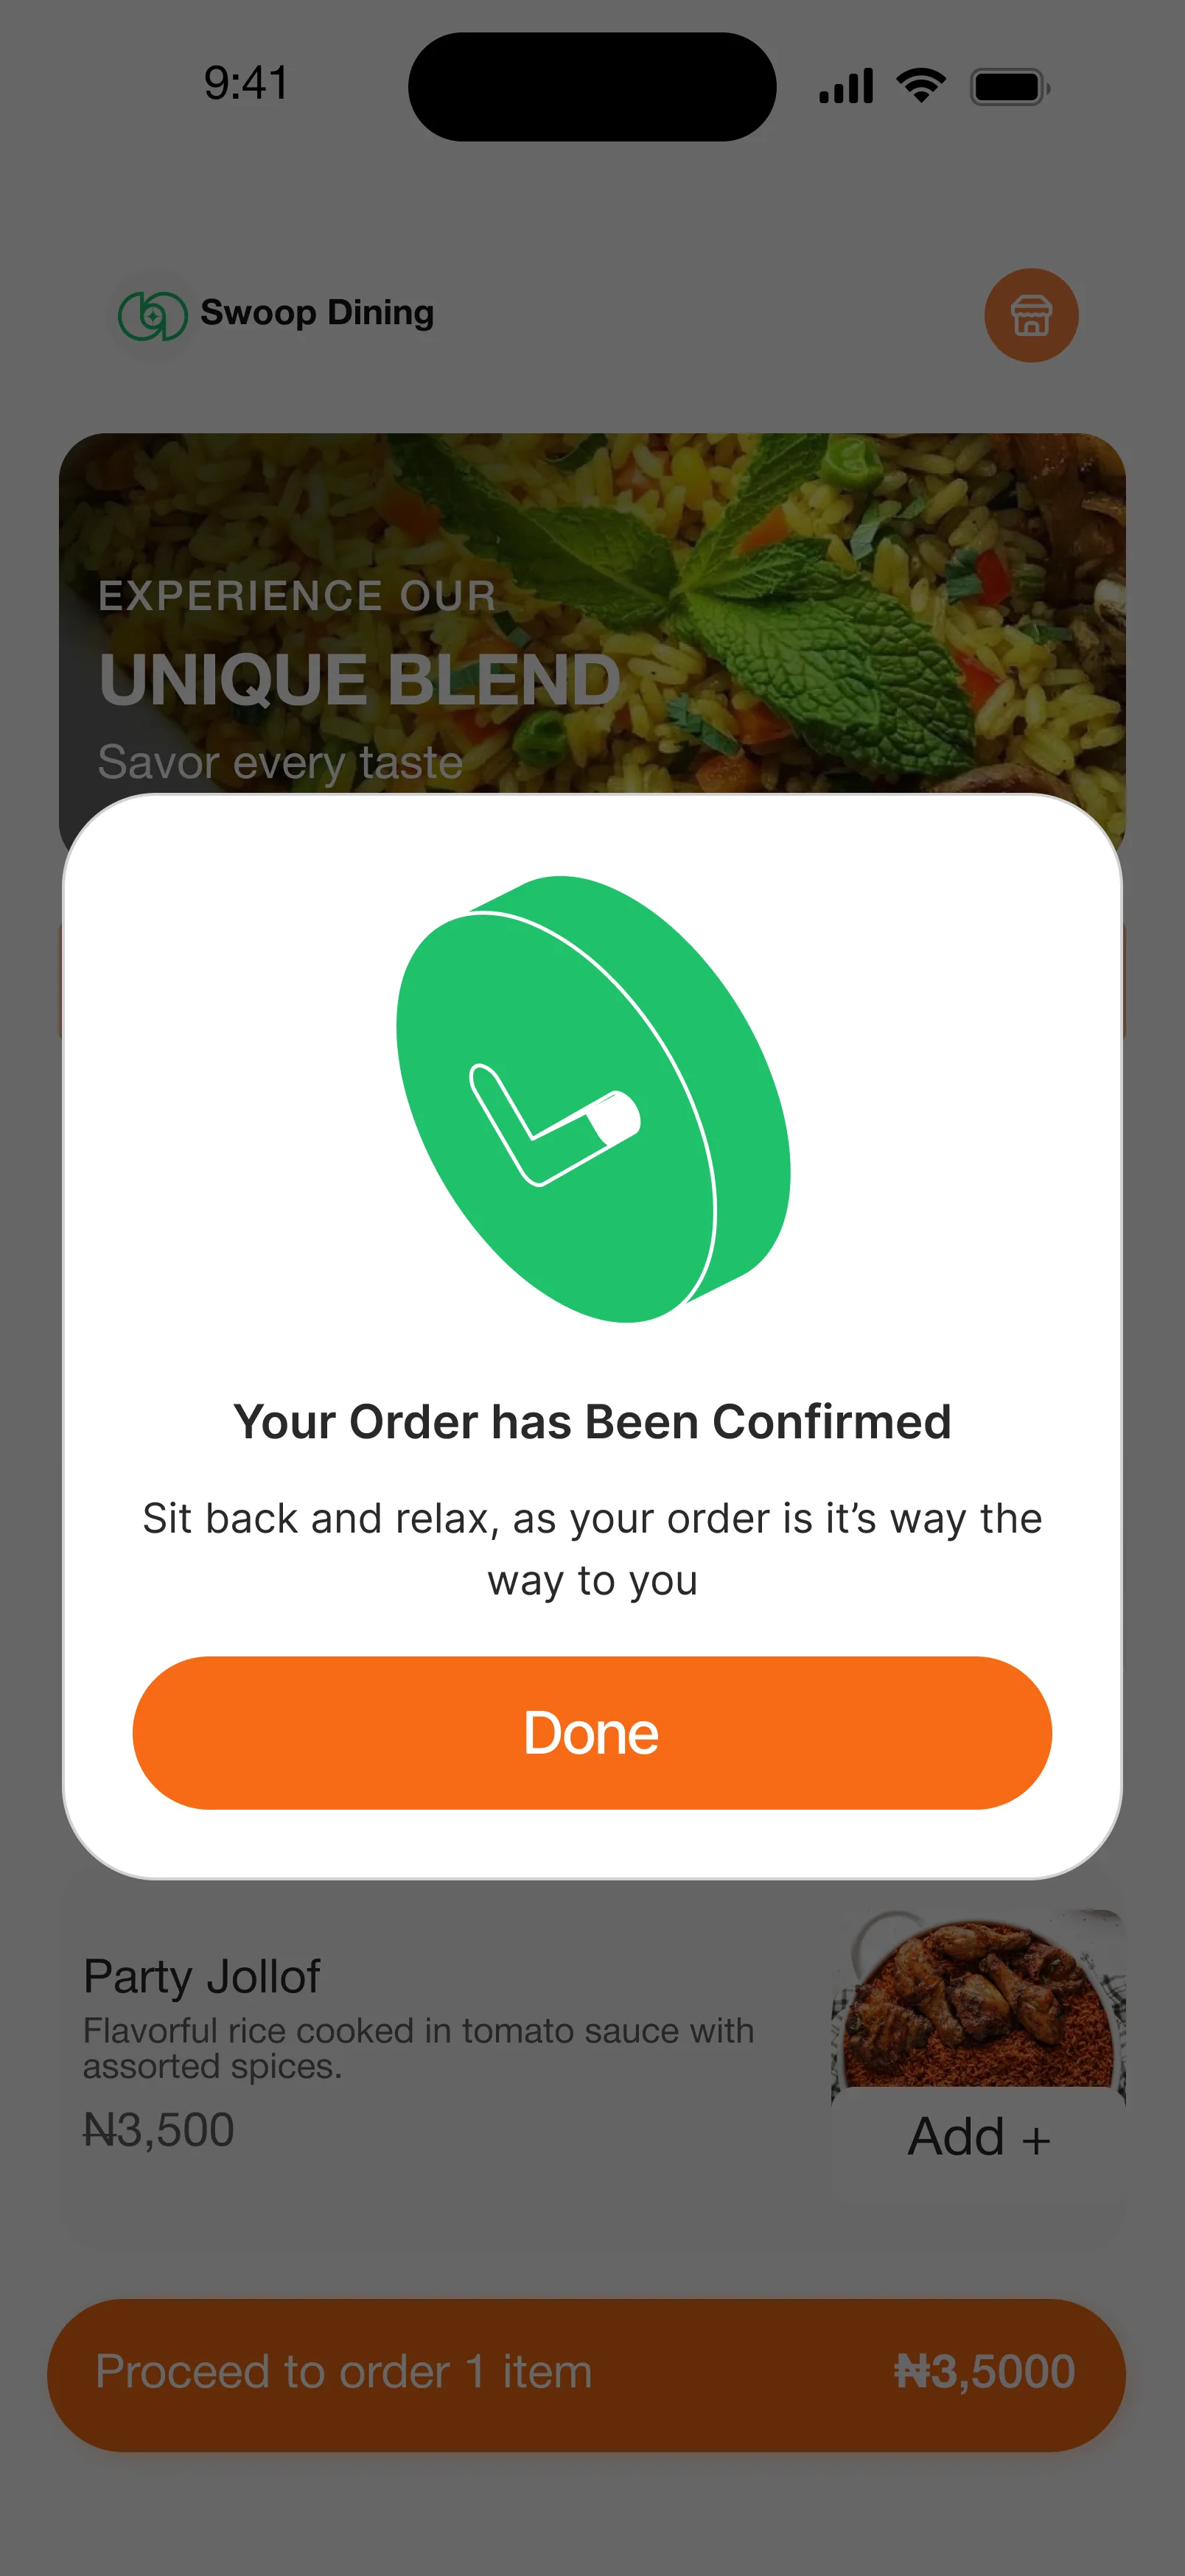
QR-driven restaurant ordering engine: polyglot microservices with cached read replicas and live table carts.
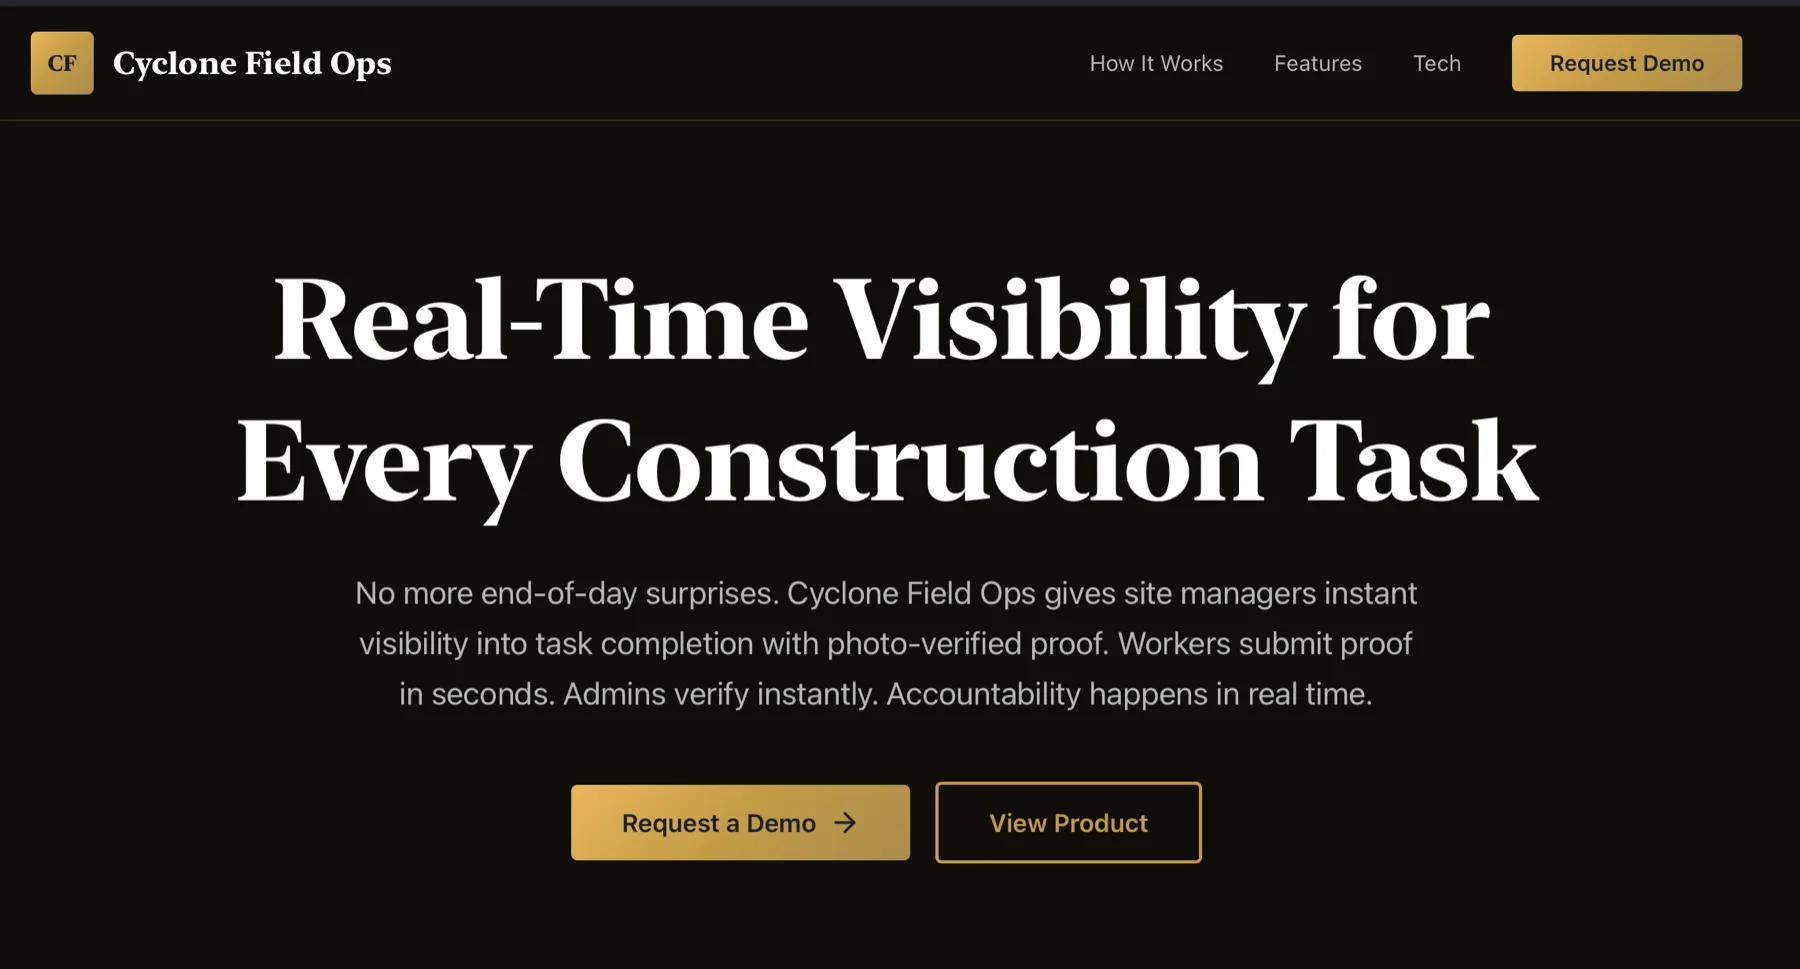
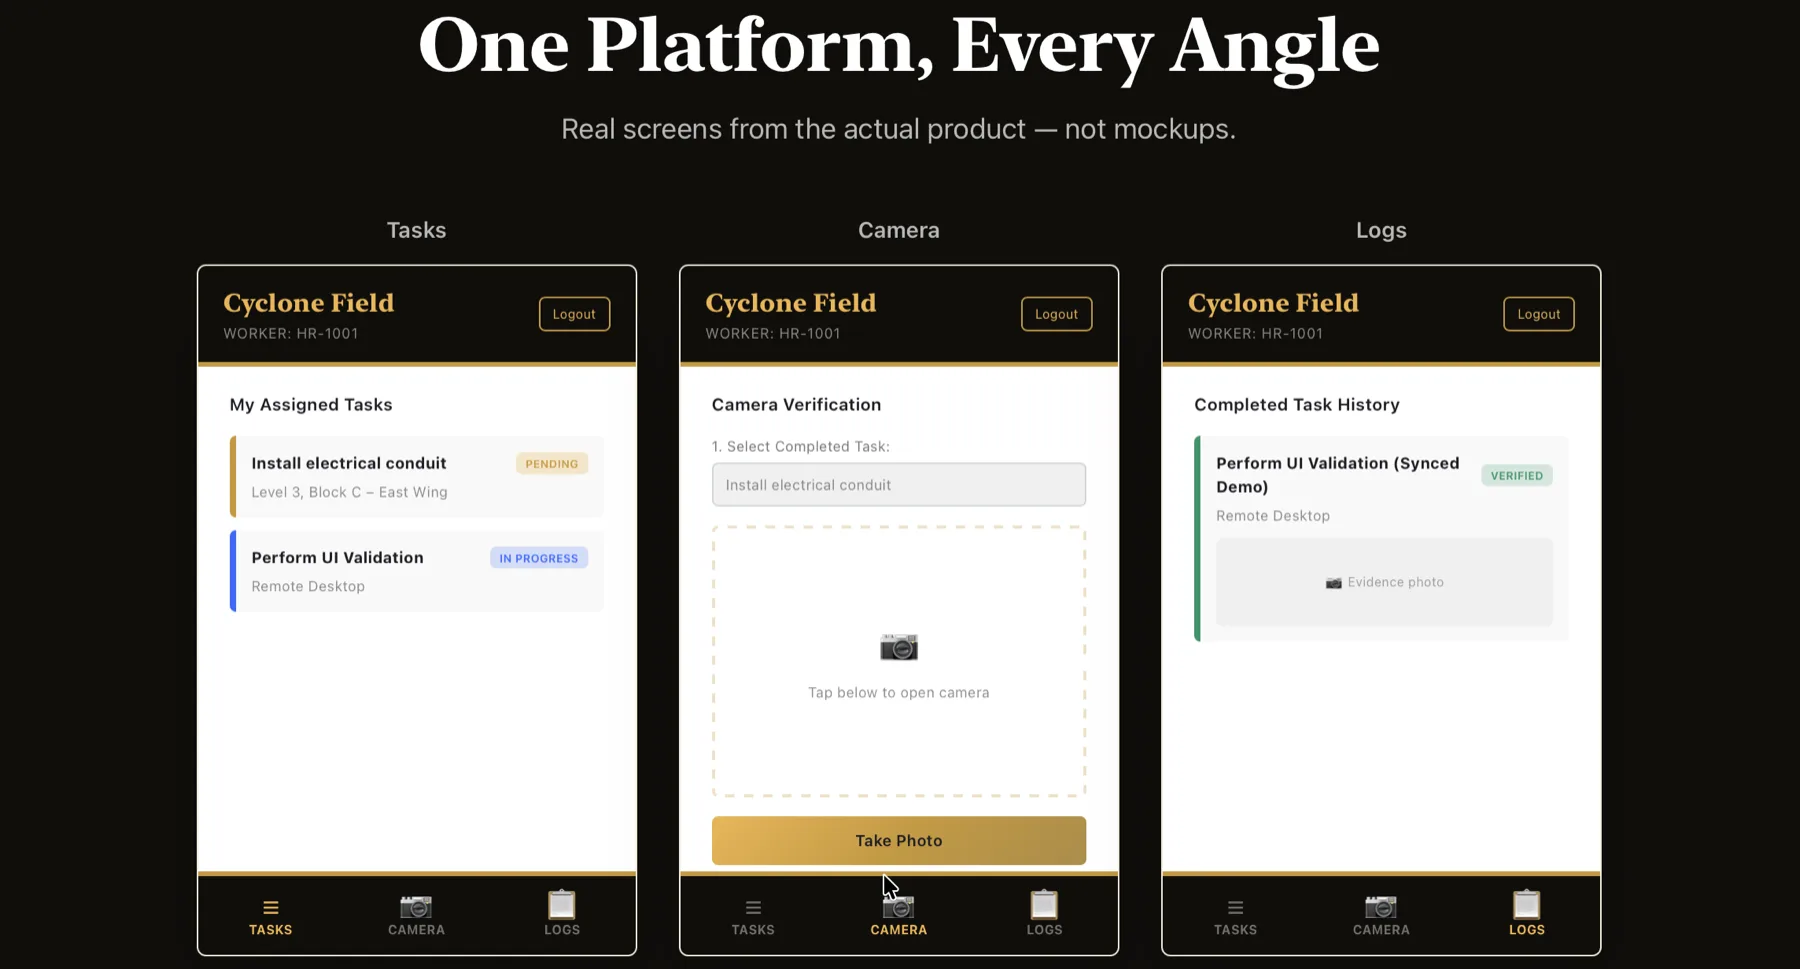
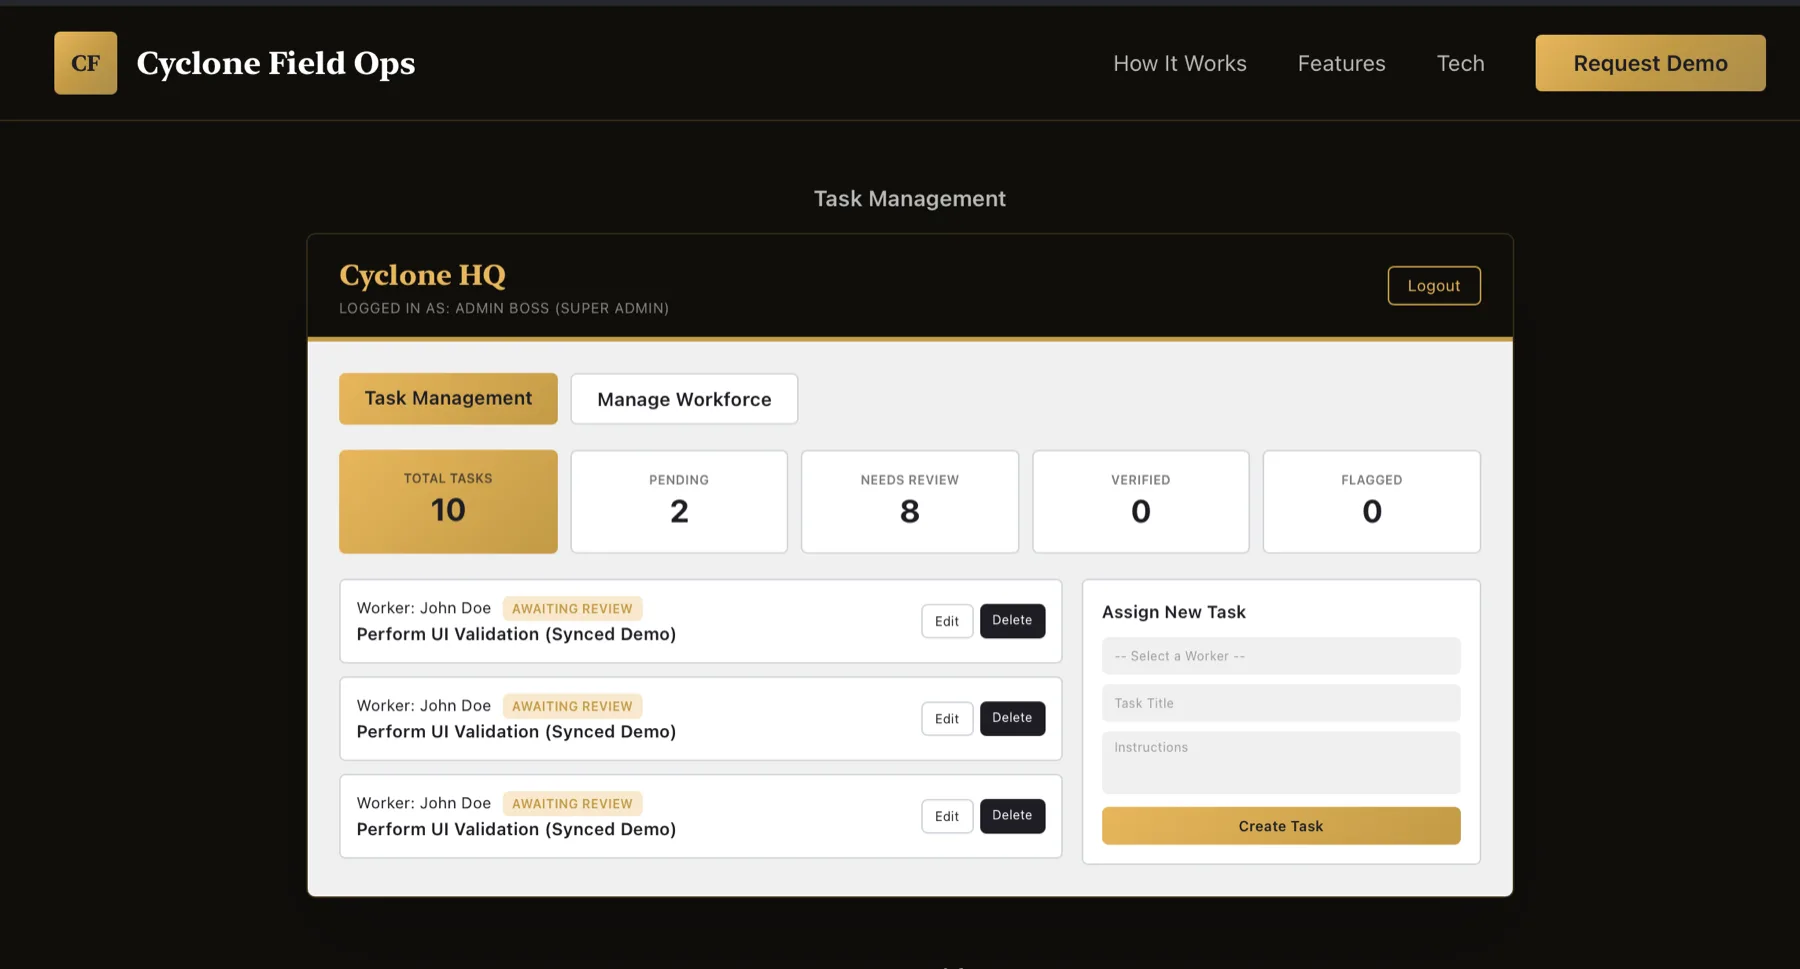
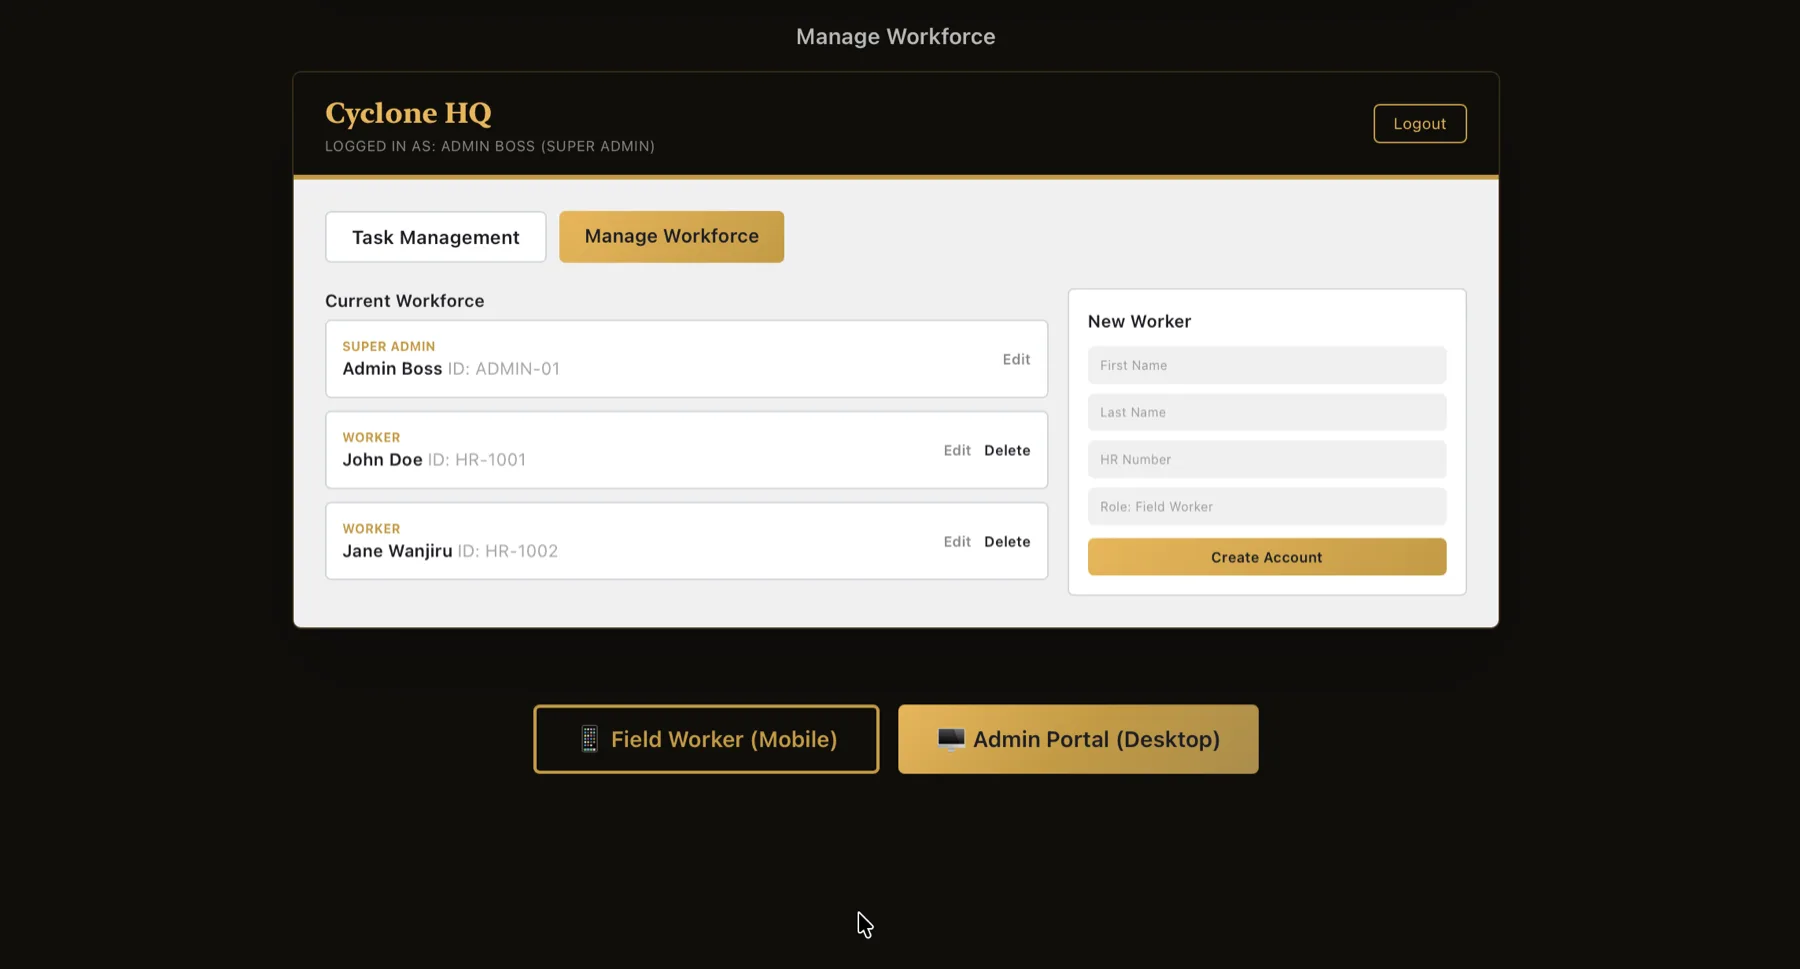
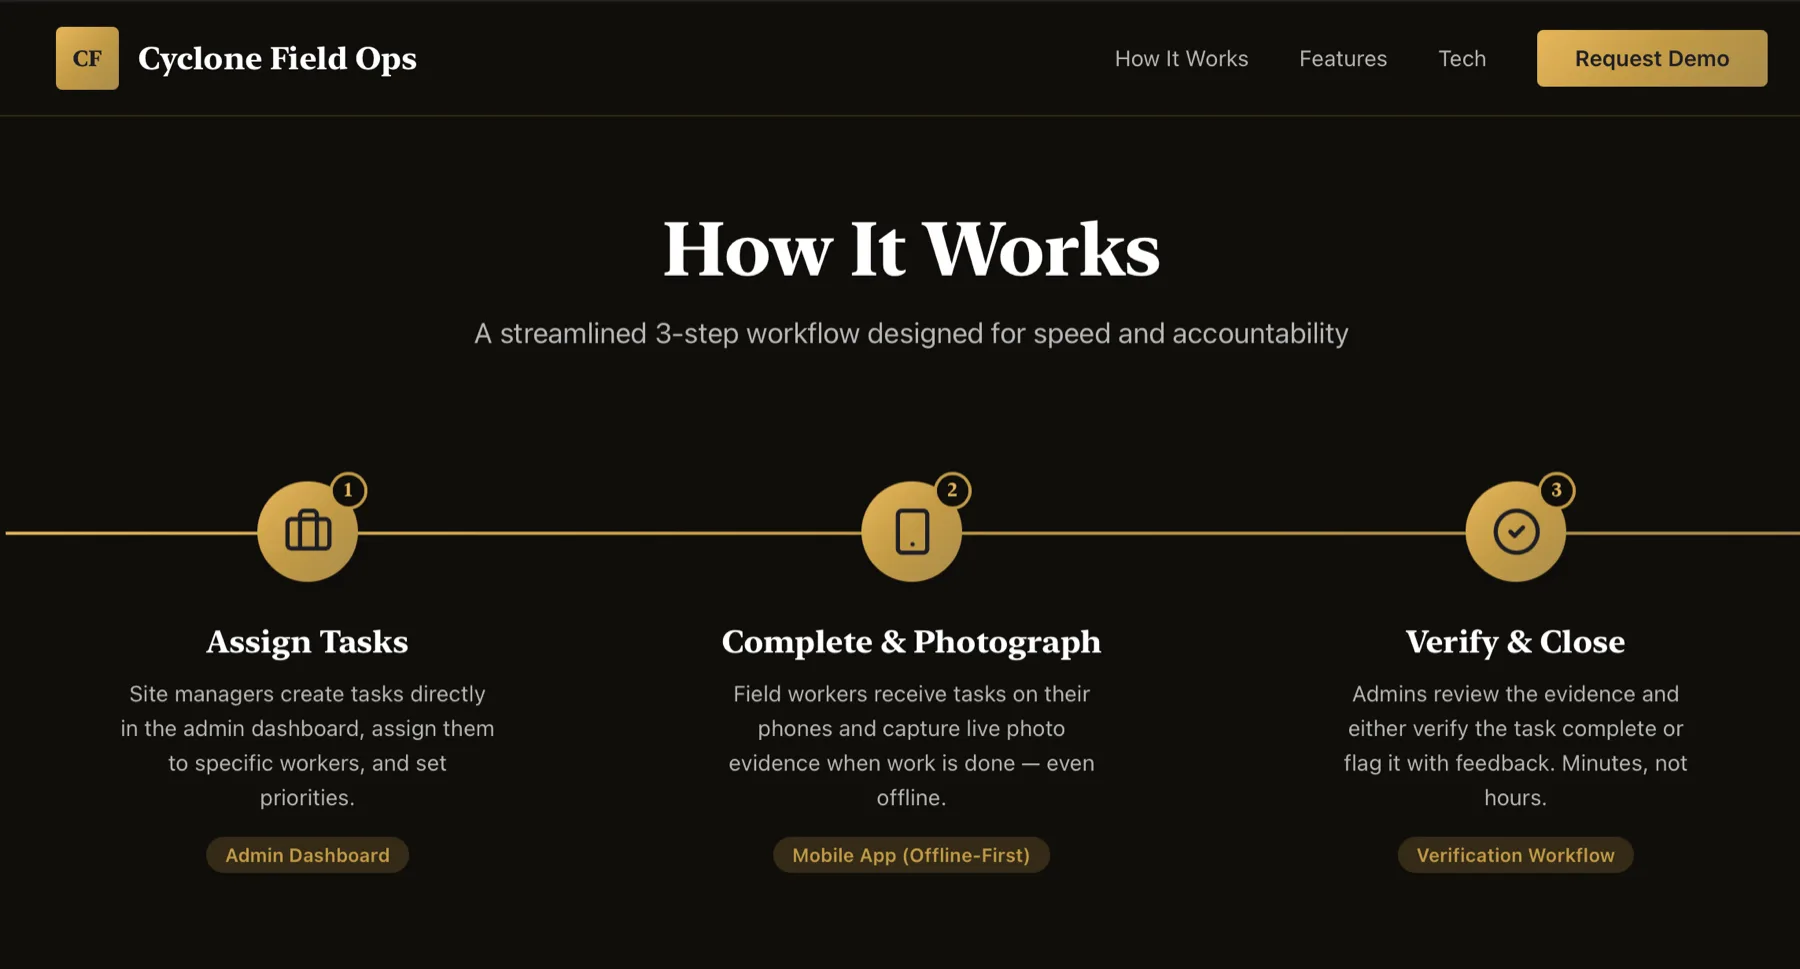
Offline construction verification engine: GPS-tagged task proof, instant supervisor verification, and automated audit state machines.
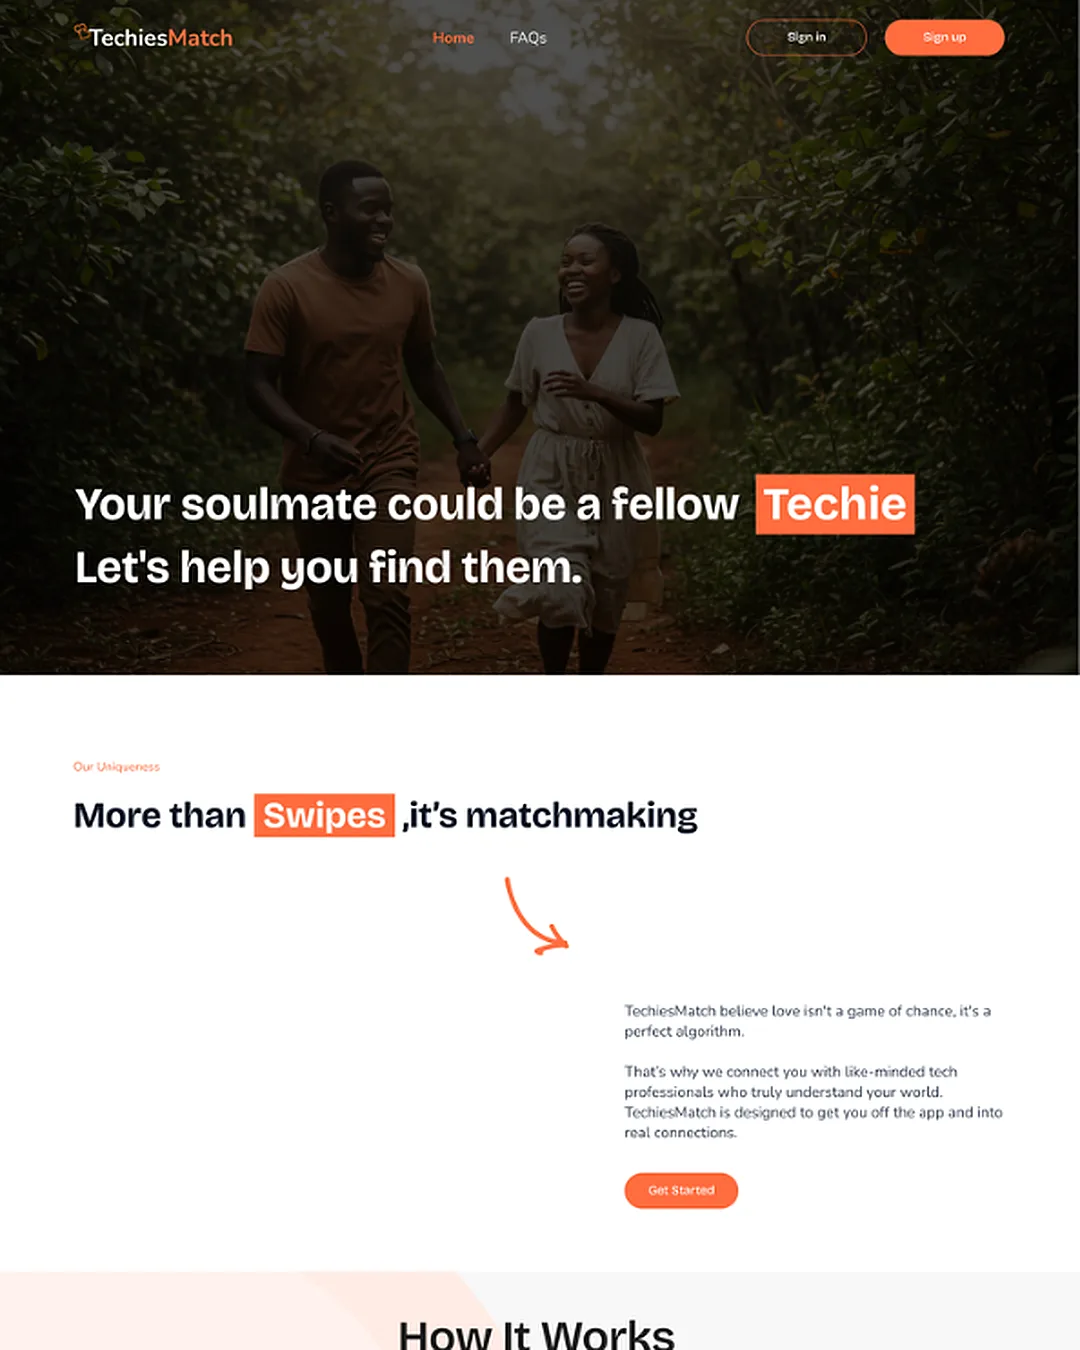
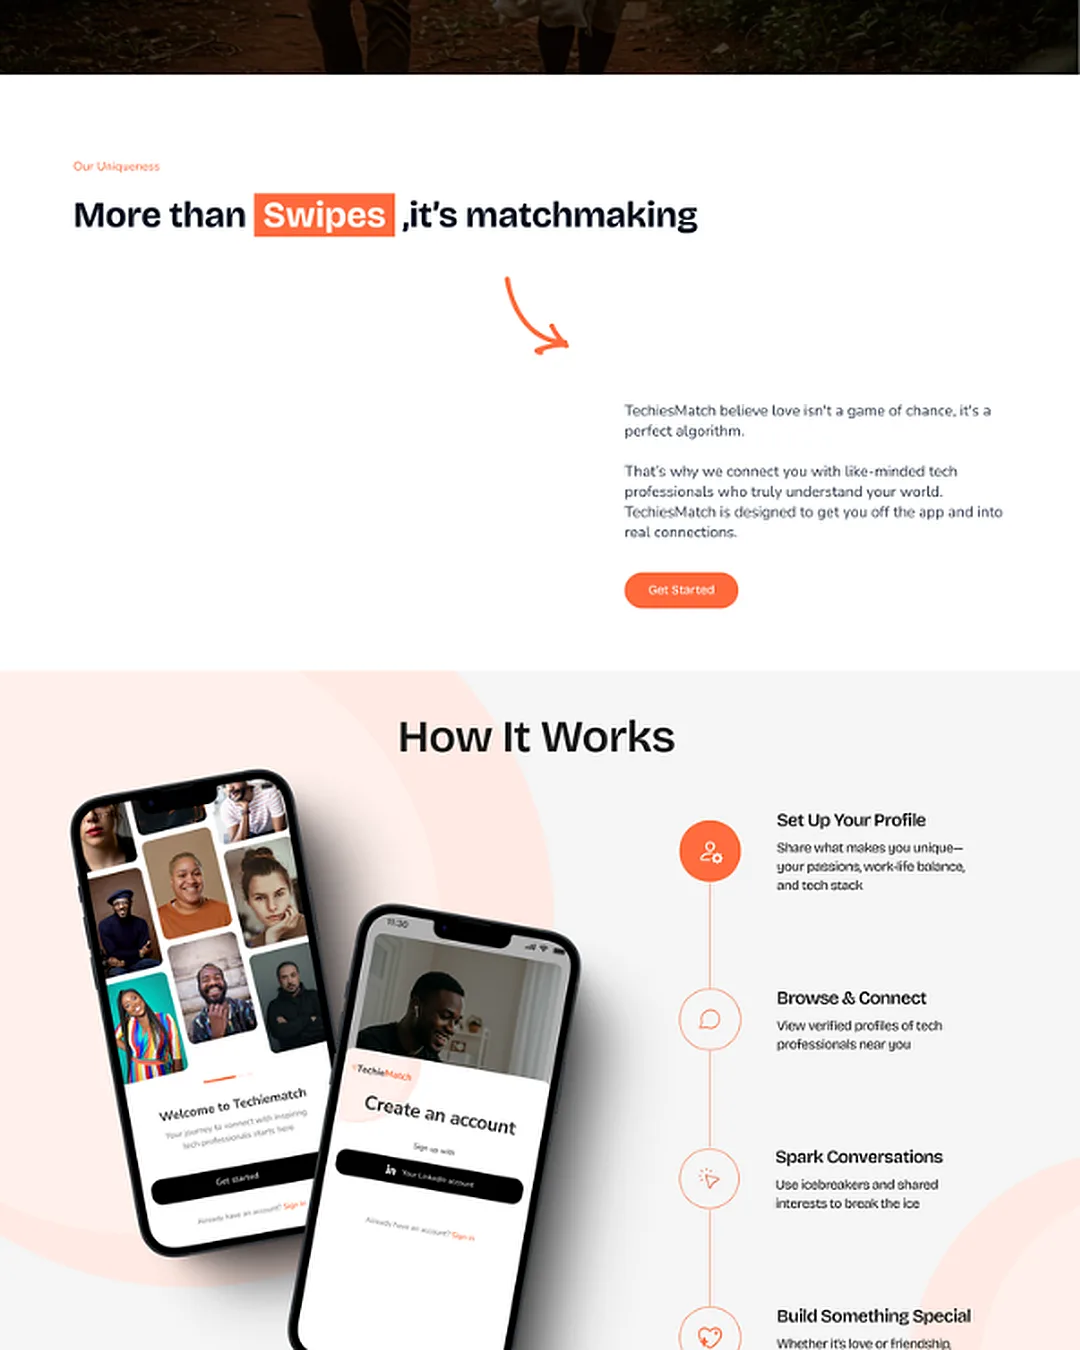
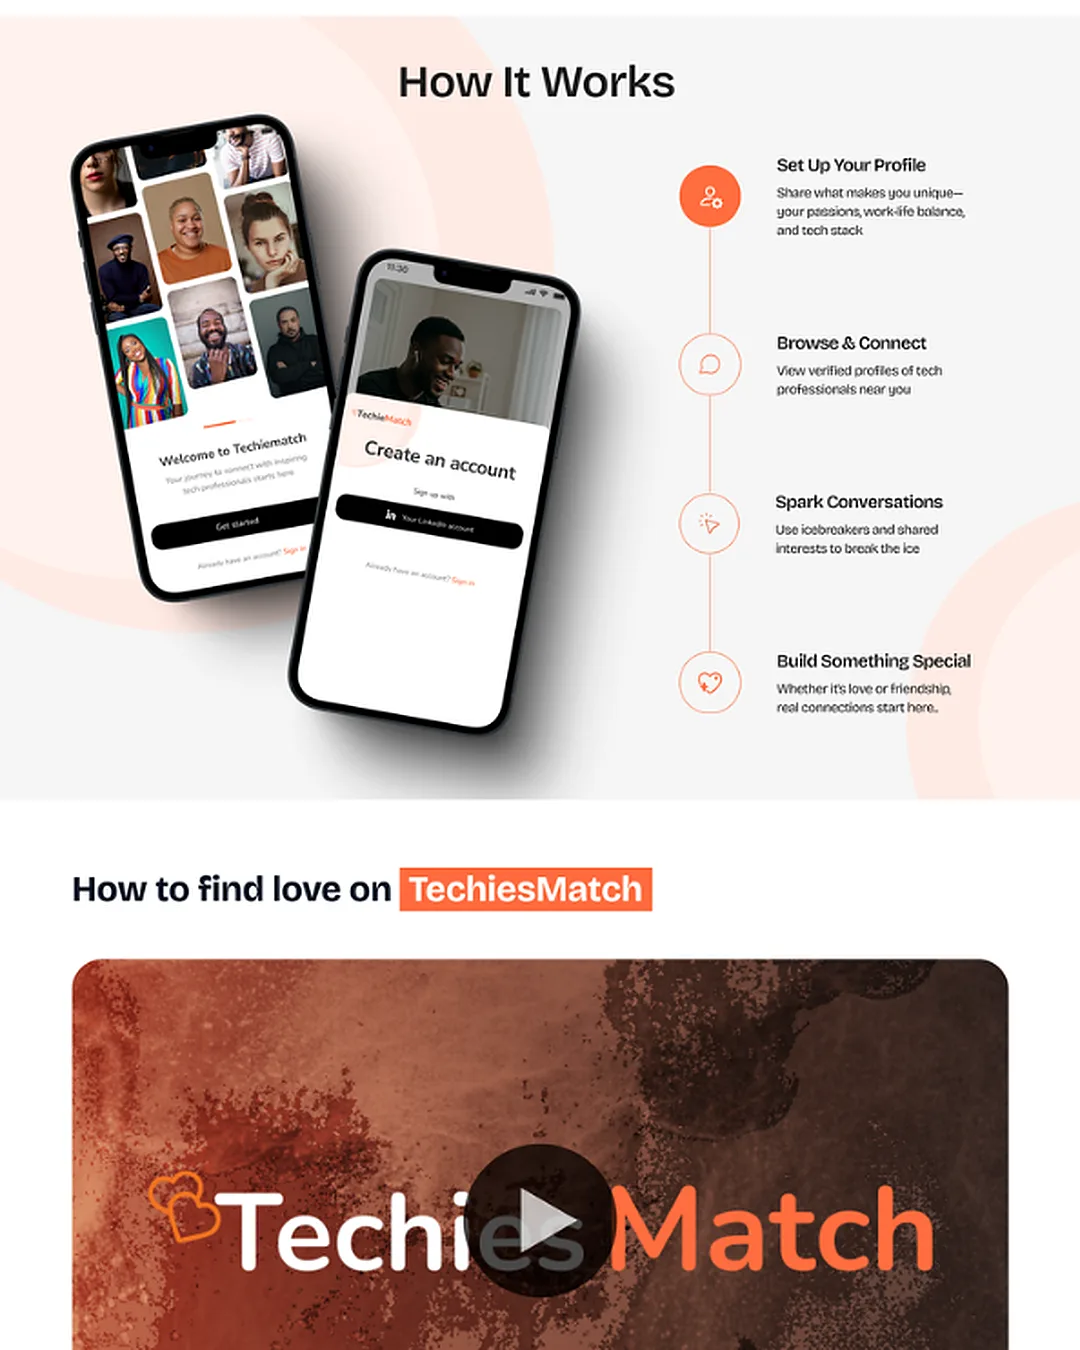
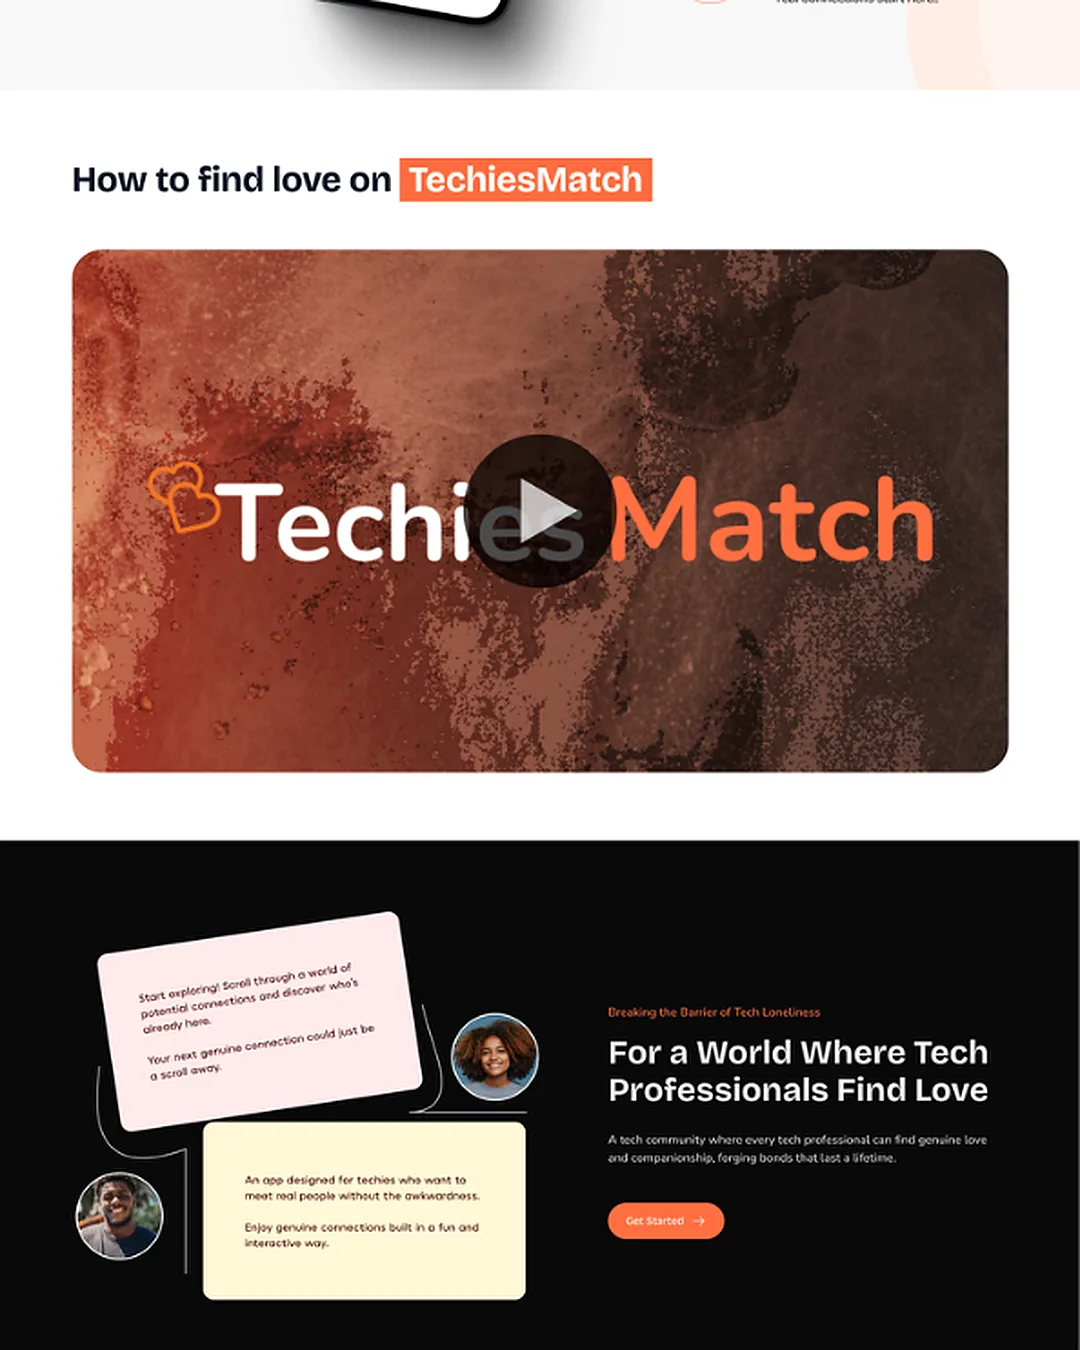
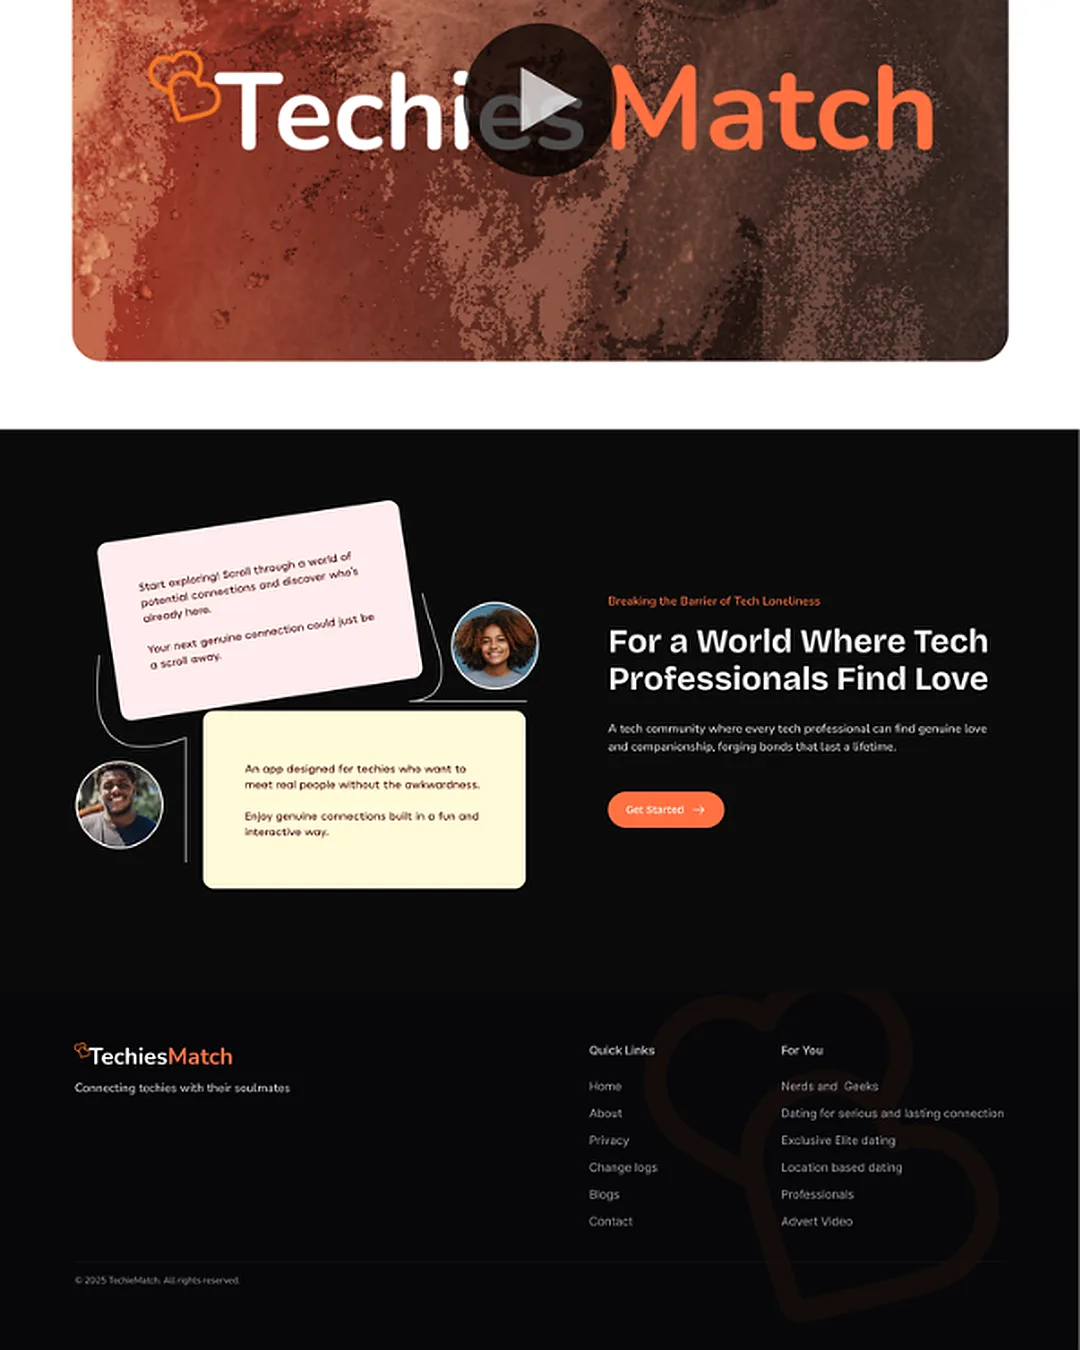
Real-time matchmaking platform connecting tech professionals for collaboration and networking.
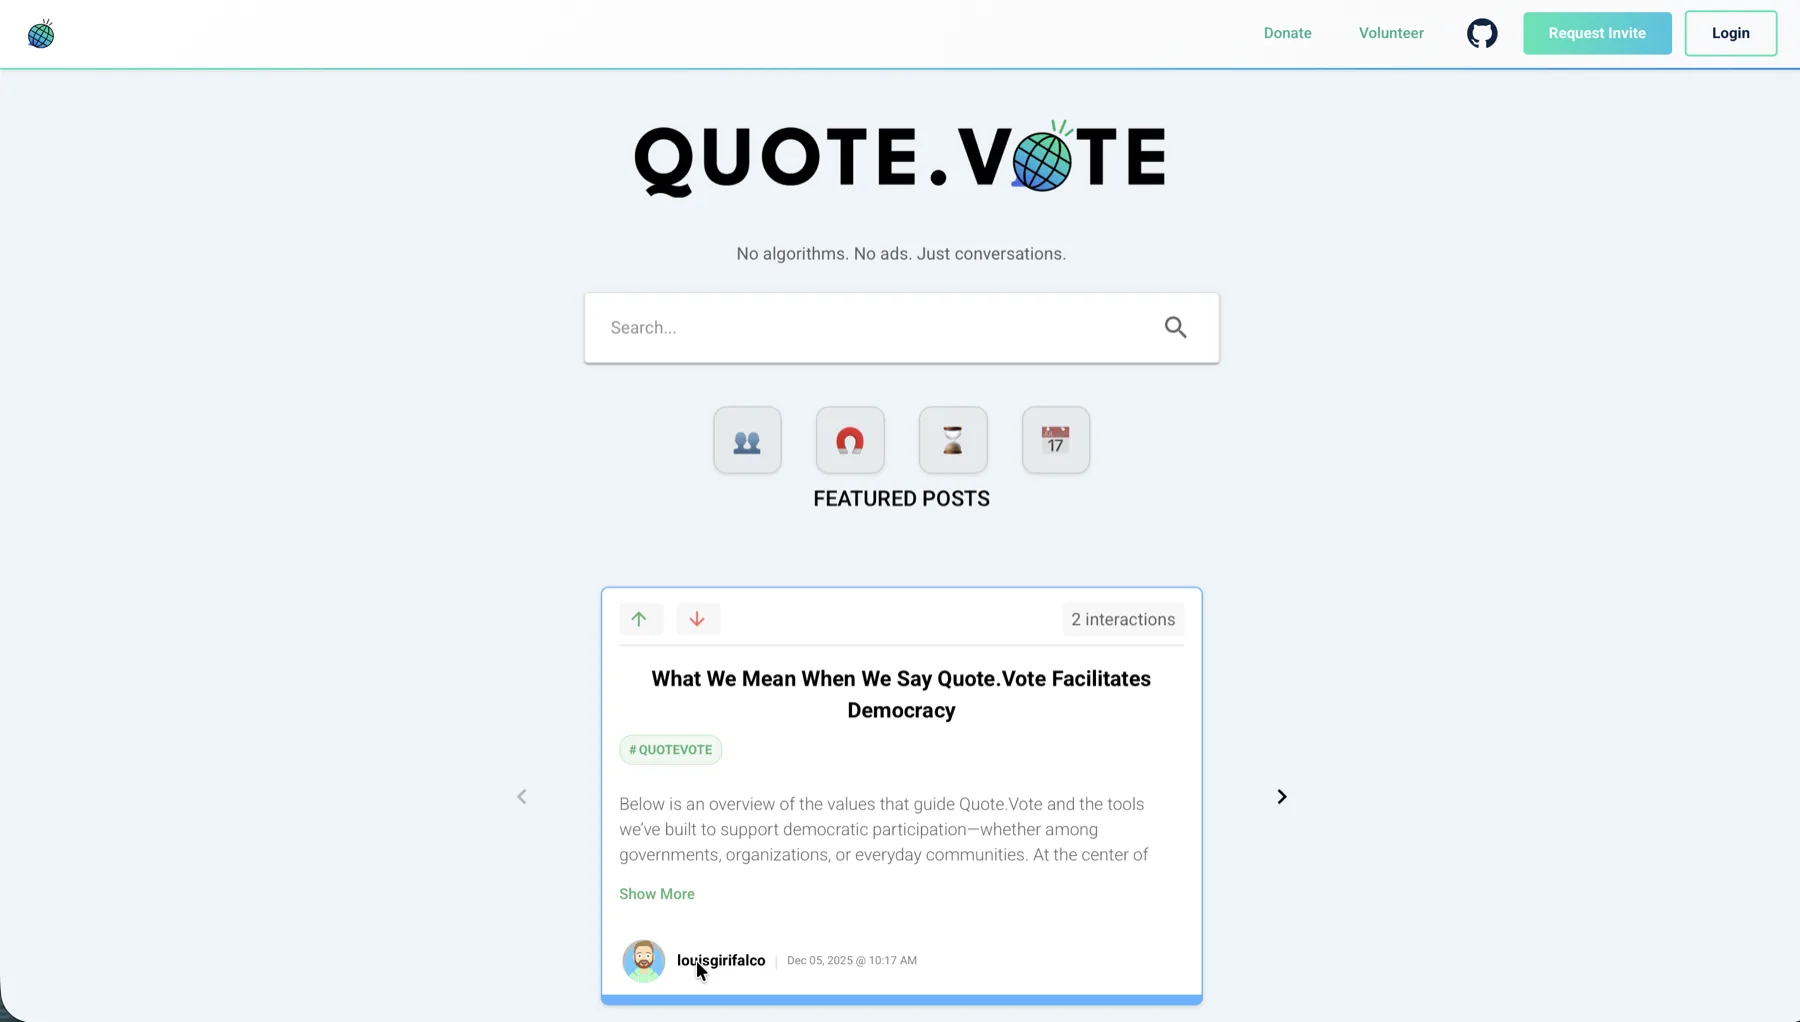
Open-source public square for civil dialogue — post quotes, vote, and deliberate.
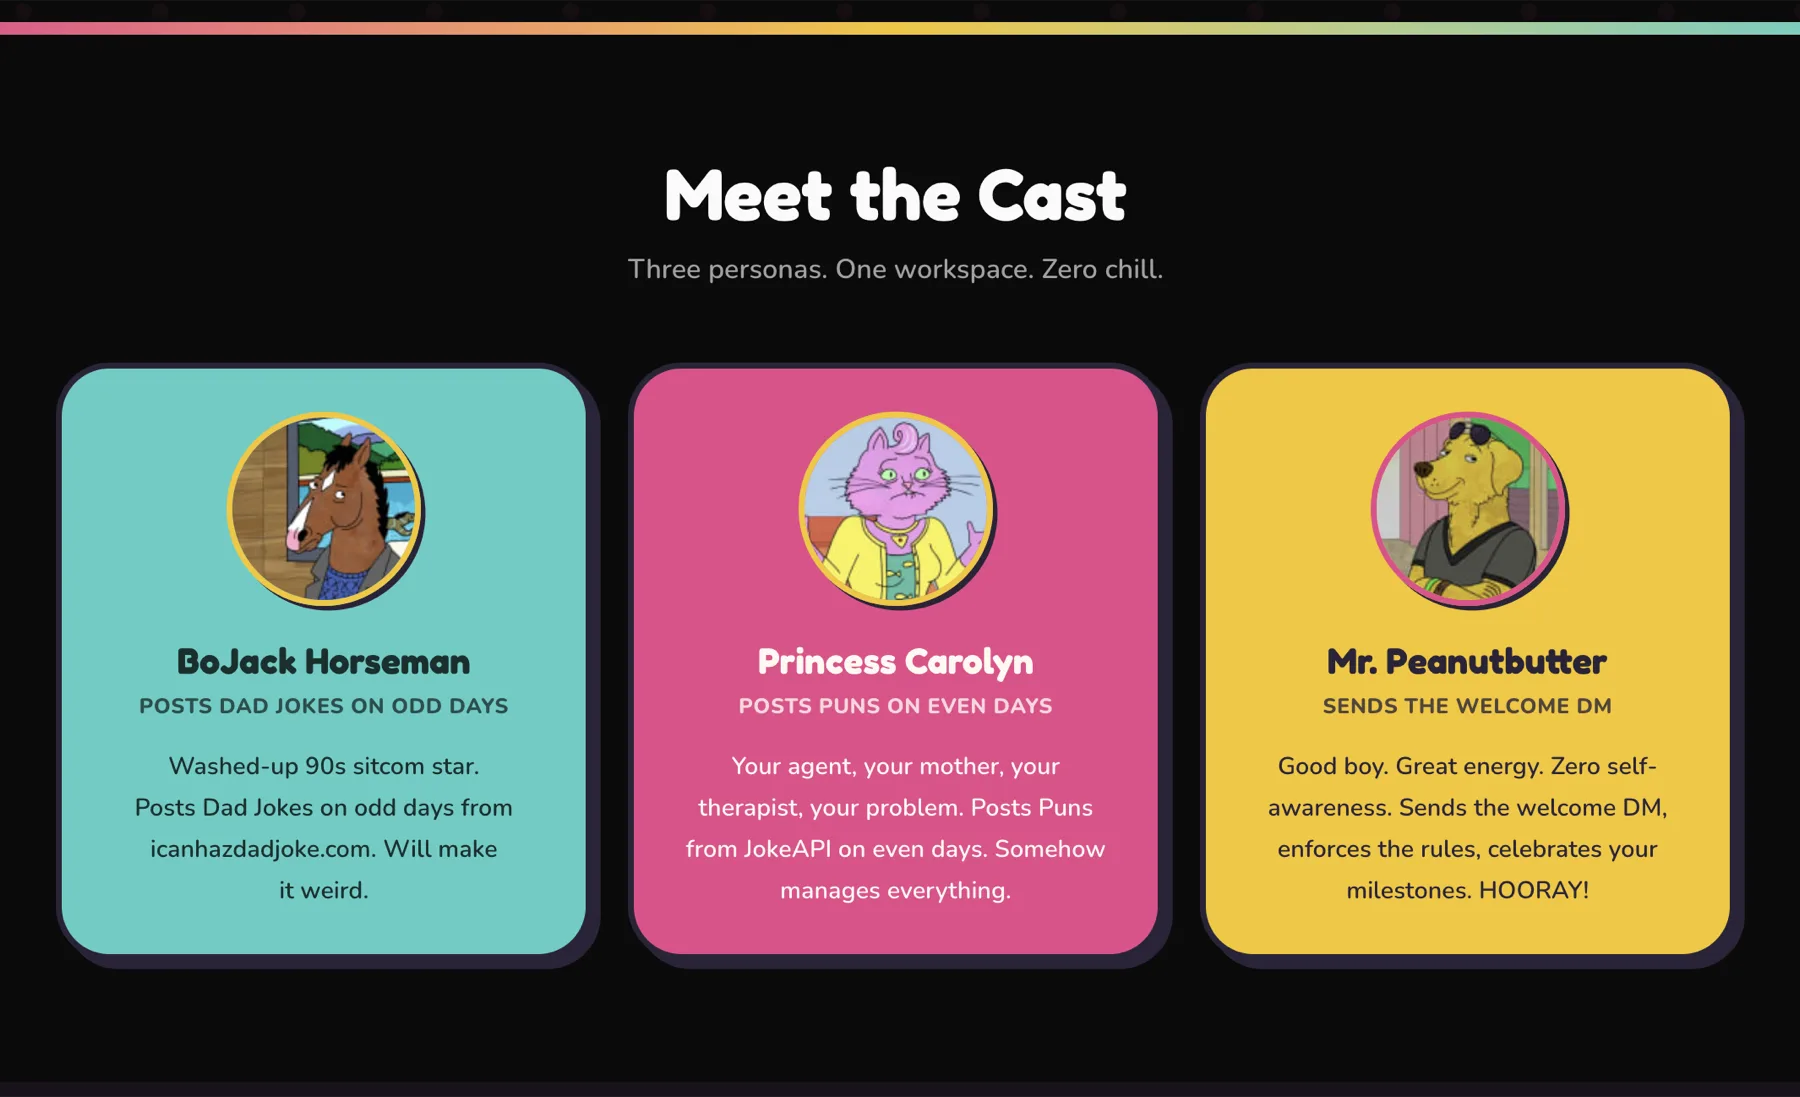
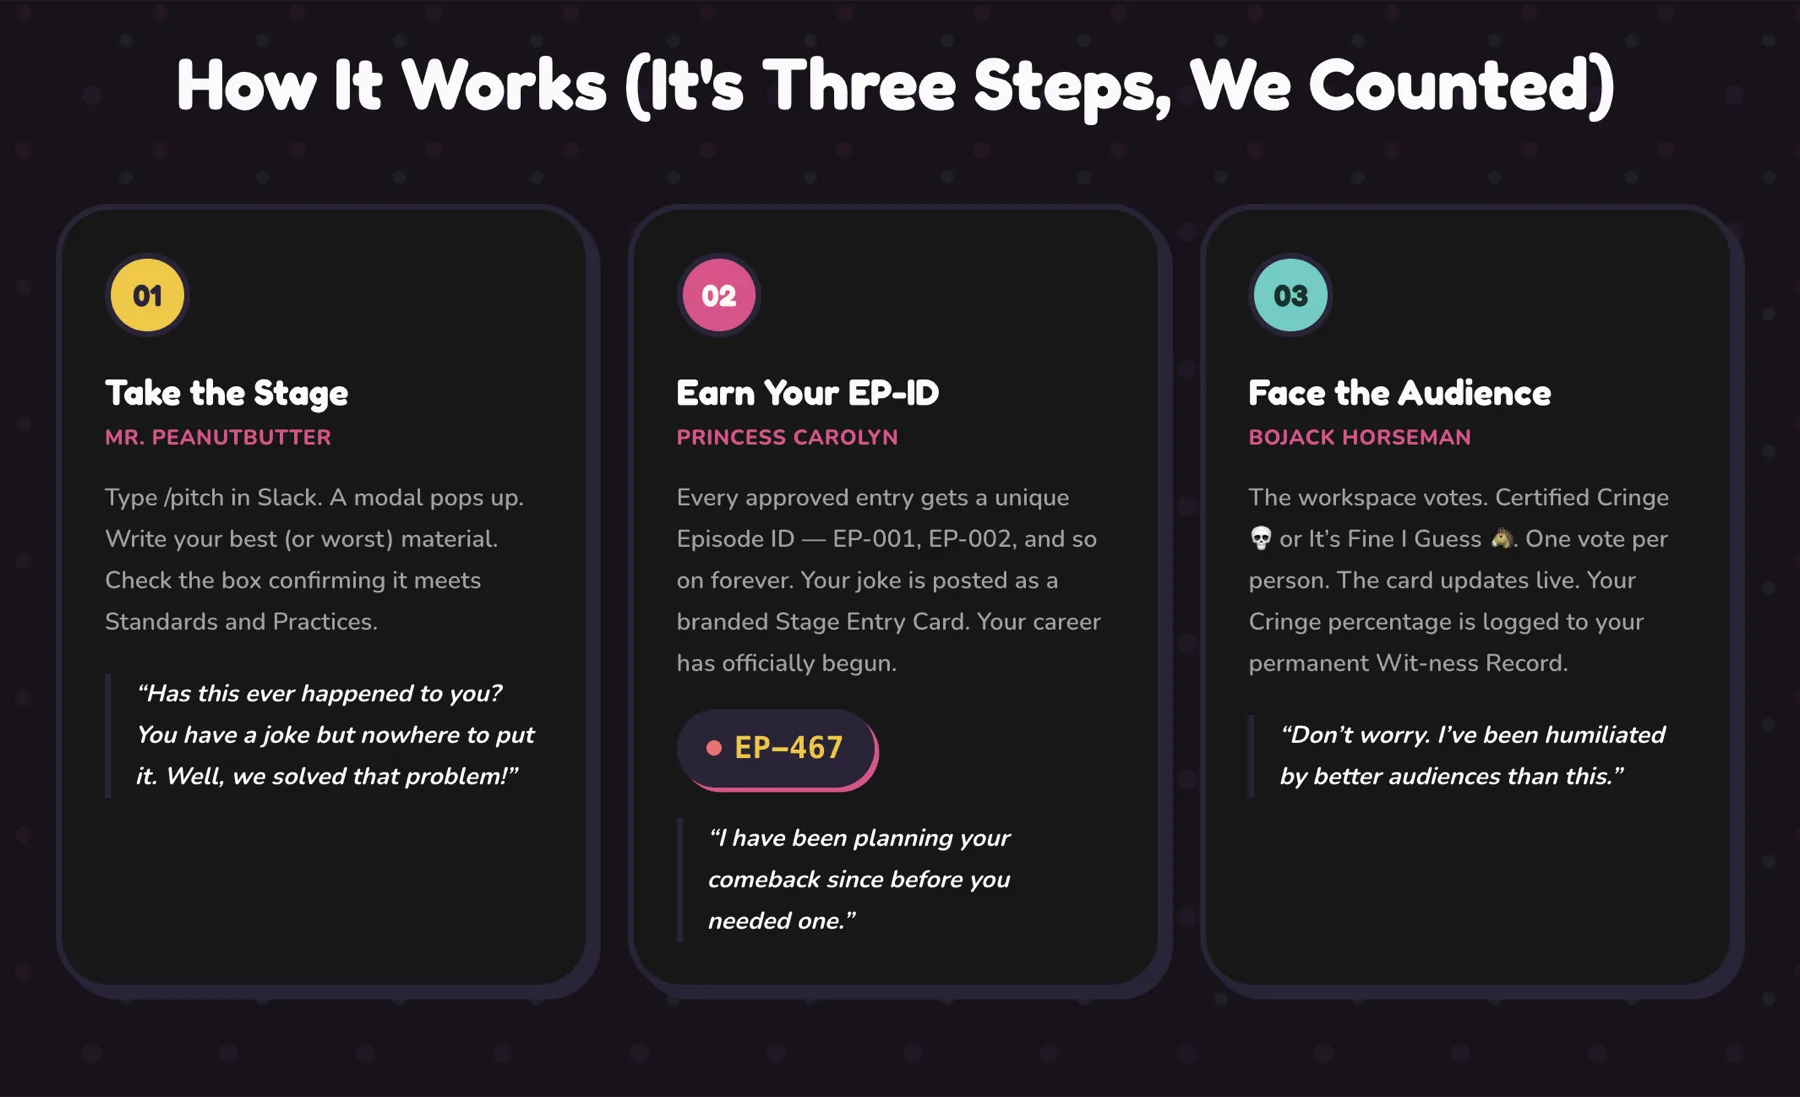
A comedy channel bot for Slack, styled as a tribute to Horsin' Around — the fictional sitcom-within-a-show from BoJack Horseman.
Zero-trust GitOps publishing engine: a browser studio for editors and a CLI for engineers, both converging on a JWT-signed GitHub PR and review gate before a zero-downtime Dokploy deploy. CMS ease without the database, the attack surface, or the developer bottleneck.

Full-stack wedding planning dashboard — guest manager, action plan, vendor management.
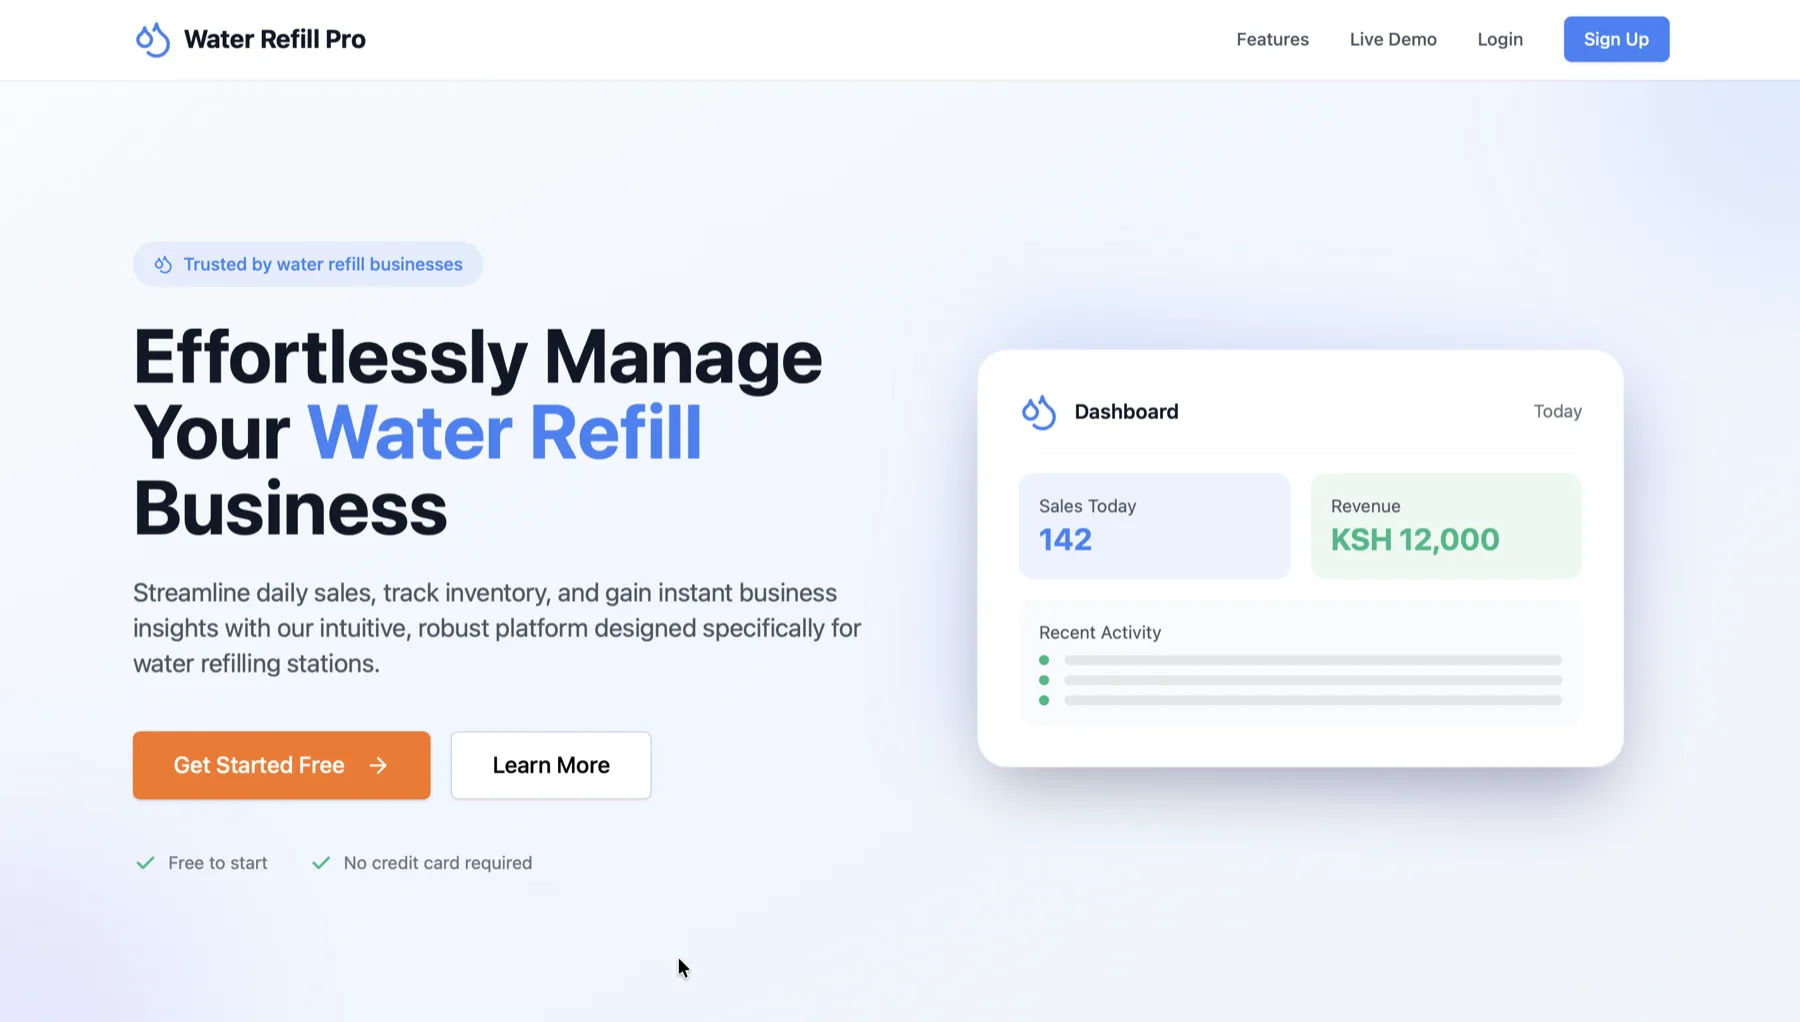
Business management for water refilling stations — daily sales, inventory and revenue dashboards.


Commercial corporate website for mineral exploration and extraction services — headless static architecture and edge CDN delivery.

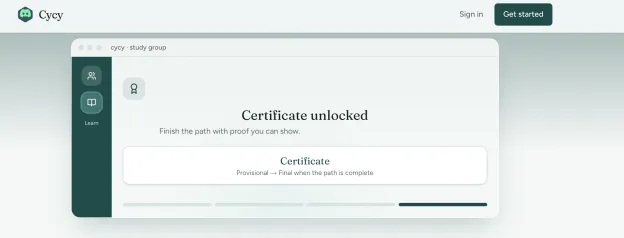
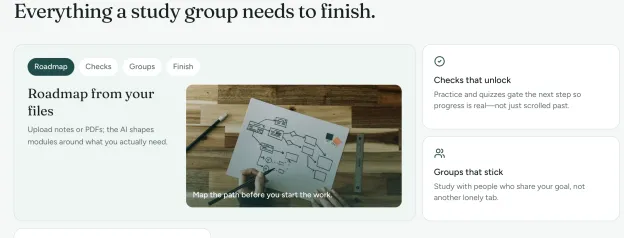
AI-powered study group platform — automated roadmaps, milestone gate checks, and certificates.

Event site for Africa's premier tech conference — countdown, speakers, schedule, ticket pricing.

AI climate resilience dashboard — disease detection, crop monitoring, sustainability rewards.
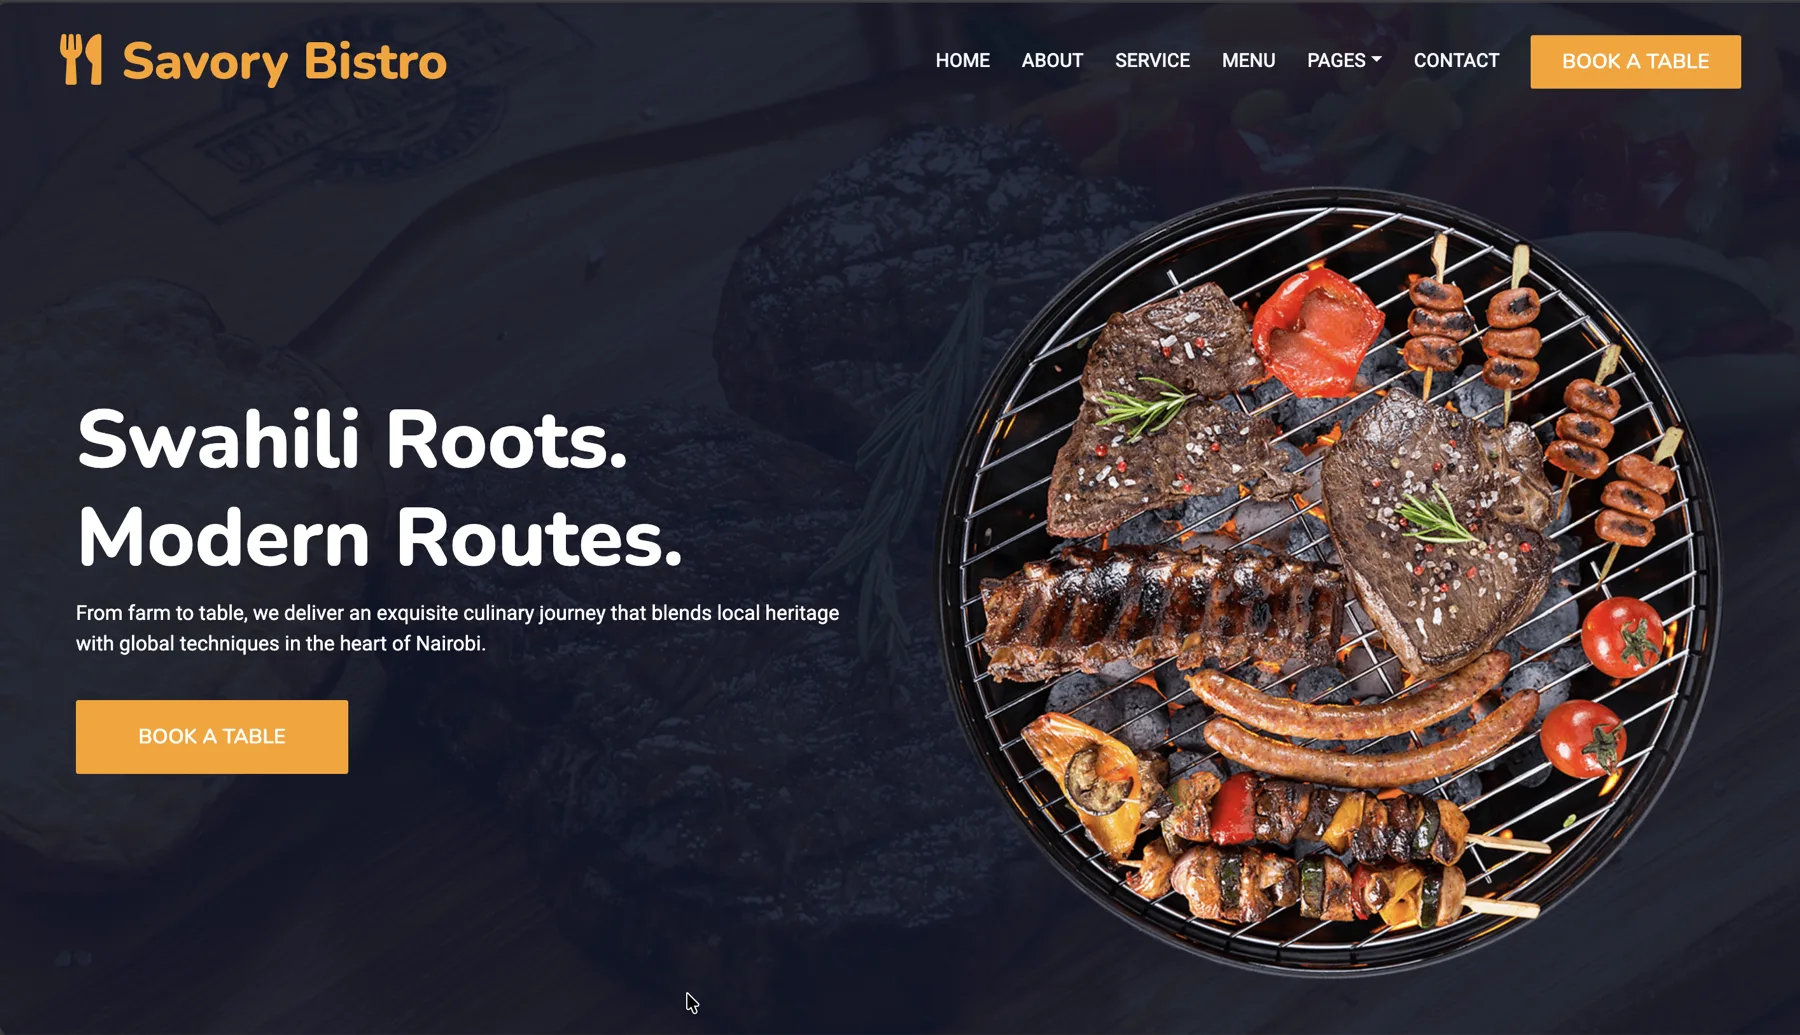
Full-featured restaurant site with attendant dashboard, reservations, and order management.
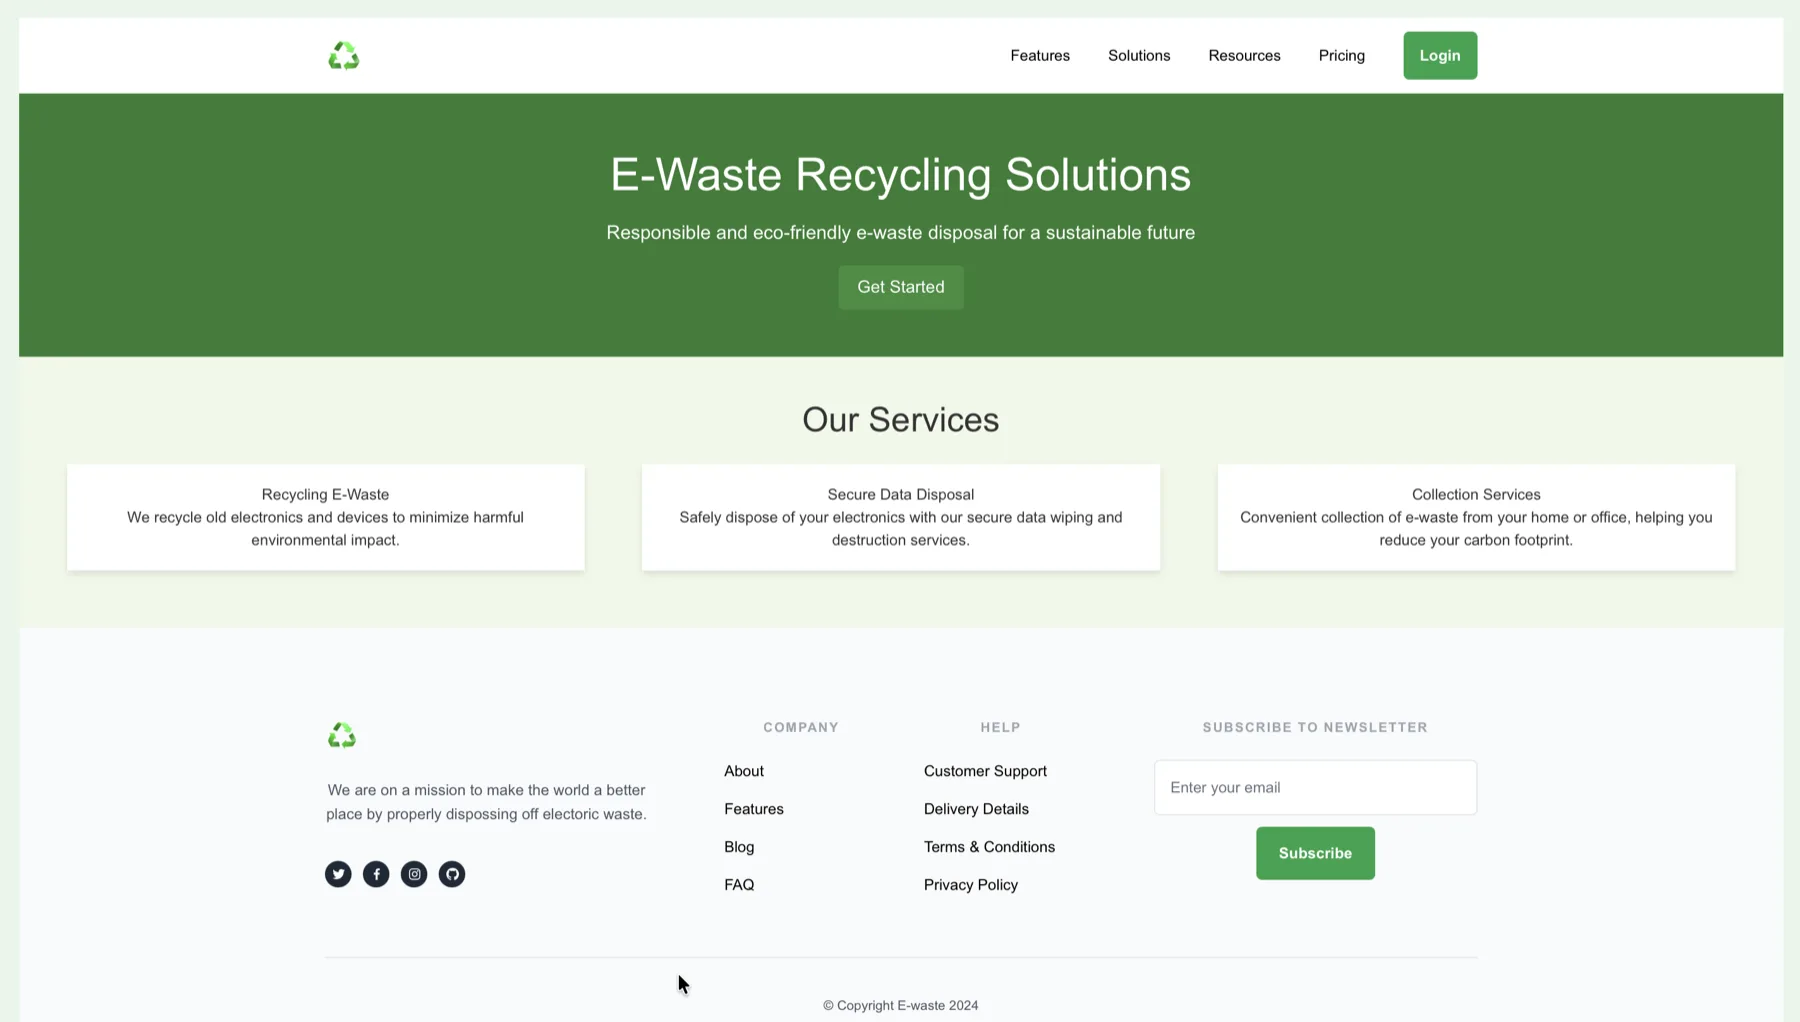
Schedule e-waste pickups and track collection in real-time — user and collector roles.
Led it. Shipped it. Slept eventually.
Automate once. Suffer never.
Articles written after the fire.
One stolen admin token reached every repo. So I built a release that needs two people, and found four bugs only by running it.

I was assigned two tests. Going test-first found a missing field, a misleading error and tests that never ran.

A Swahili proverb: seal the crack or rebuild the wall. Backend first principles from cleaning up a production codebase.
Also worth a read:
Not just listed. Actually used.


Aligned, justified, certified.
 See all open source badges →
 See all community badges →
 See all certifications →
Bring a problem.

If you'd rather prevent fires than fight them at 3am, we'll get
along.
Let's build systems that make
production boring.
or find me here